3 November 2026
|6:07 pm
|Aanetic Advisory Editorial
Looking for faster SOC 2 certification? Explore how the right compliance provider can simplify audits, reduce delays, and accelerate your SOC 2 journey.
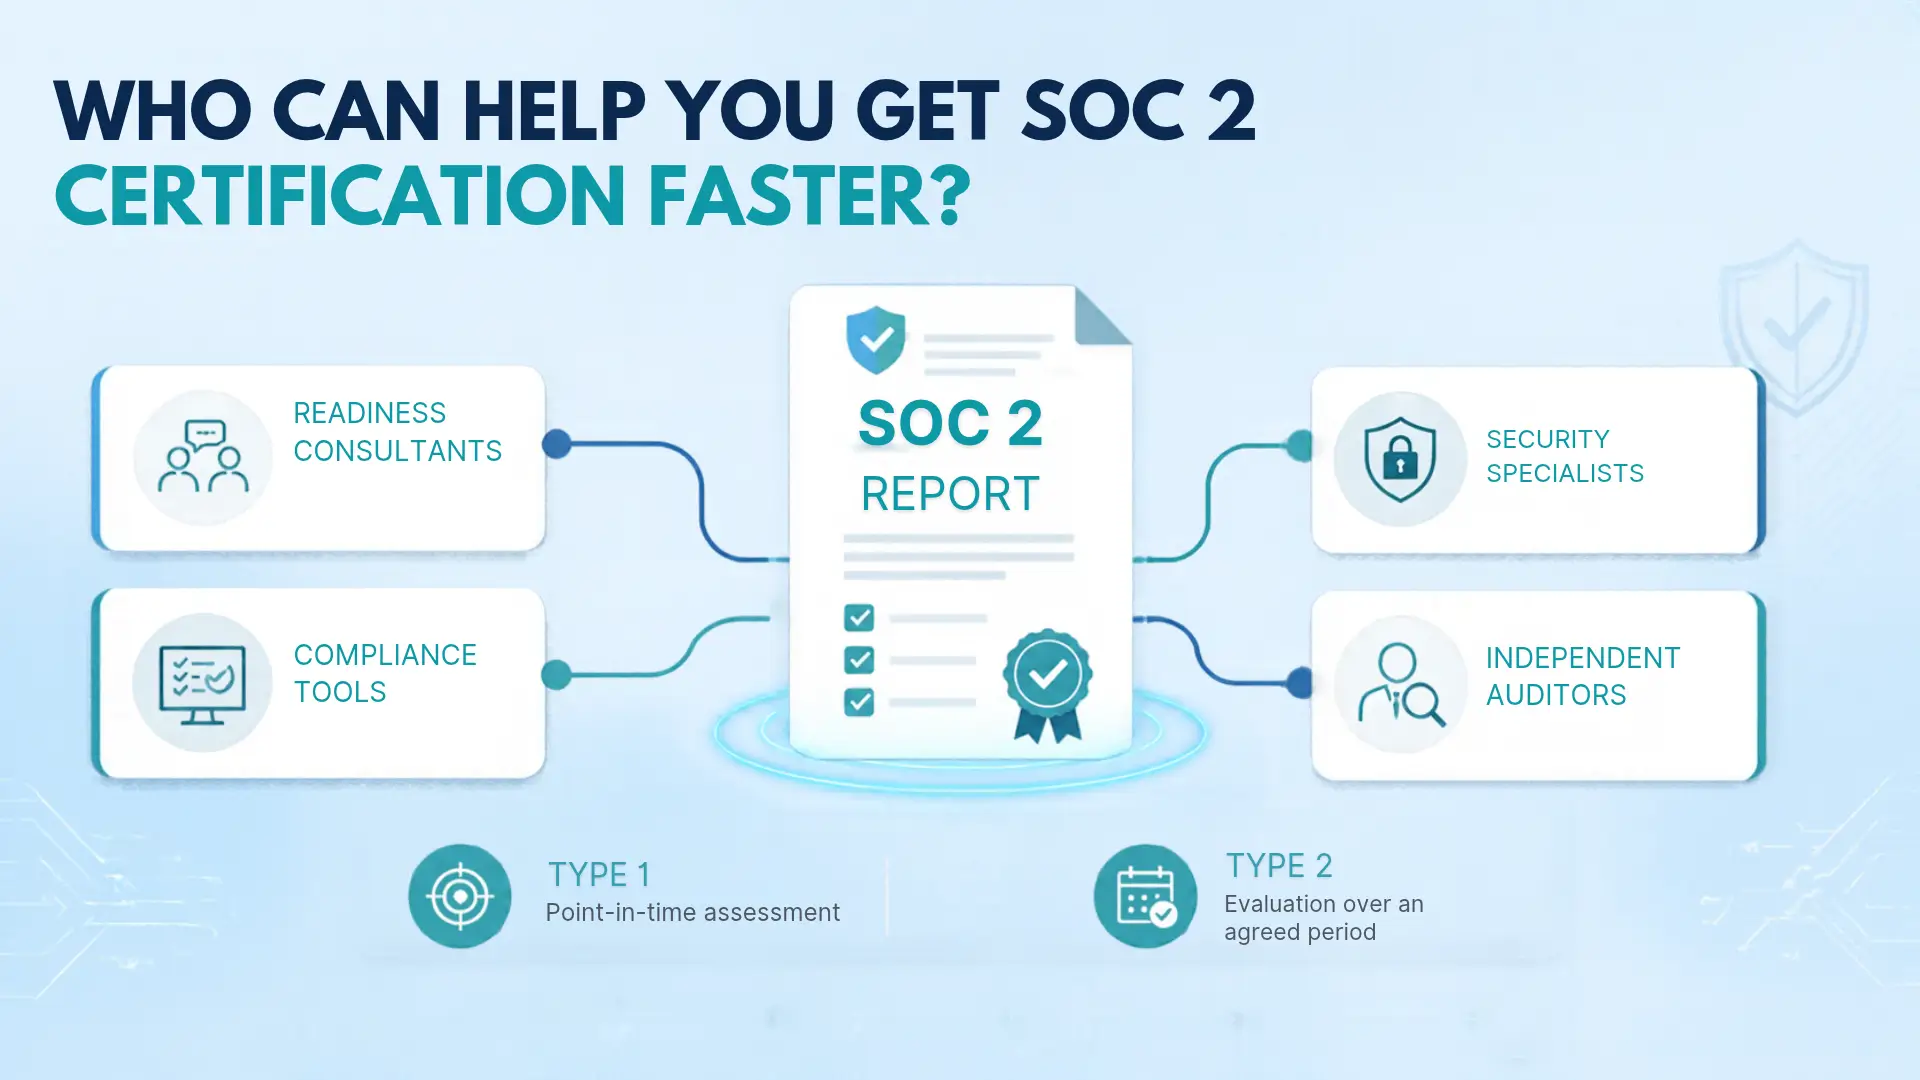
Getting SOC 2 faster usually takes four things: an experienced readiness consultant, a compliance automation platform, committed internal control owners, and an independent CPA firm as your service auditor. No provider can responsibly promise the same timeline for every organization, because your speed depends on your existing controls, evidence, report type, and remaining gaps.
Indian SaaS startups, fintech companies, cloud service providers, and IT businesses often face SOC 2 certification requests during enterprise procurement or vendor security reviews. The right support organizes your preparation, closes gaps early, and removes avoidable delays, while preserving the independent examination that makes a SOC 2 report credible.
A faster SOC 2 certification process means completing the necessary activities efficiently, not skipping requirements or receiving a report immediately.
A SOC 2 readiness assessment identifies gaps between an organization's existing practices and relevant control requirements. Remediation addresses weaknesses in policies, procedures, systems, or in the implementation of controls. Evidence preparation organizes records that demonstrate how controls operate.
During the independent examination, a service auditor evaluates relevant controls and issues a SOC 2 report once the engagement requirements are met.
A readiness provider can accelerate planning and coordination, but cannot replace required control operations or independent auditor work. Reducing avoidable delays is more reliable than choosing a provider solely because of an advertised timeline.
Readiness consultants assess existing controls, identify gaps, prioritize improvements, support documentation, and help businesses prepare for the independent examination.
Suitable compliance platforms can support evidence collection, task management, control tracking, and ongoing monitoring. Their usefulness depends on the features available and the organization's requirements.
These specialists help businesses address technical weaknesses, improve security practices, and align internal processes with relevant control expectations.
Independent service auditors conduct the SOC 2 examination and issue the report in accordance with applicable professional standards. Readiness consultants and automation platforms cannot replace this independent role.
Before engaging any provider, clarify its responsibilities, deliverables, fees, and approach to auditor independence.
SOC 2 Type 1 evaluates whether relevant controls are suitably designed and implemented at a specific point in time. When controls are already established and supporting evidence is organized, the examination may be completed sooner.
SOC 2 Type 2 evaluates control design and operating effectiveness over a defined period. It requires evidence showing how relevant controls operated throughout the agreed observation period, so the overall process generally takes longer.
The right report type depends on customer expectations, contractual requirements, and business needs. Type 1 may not satisfy a customer that specifically requires a Type 2 report.
Businesses can reduce avoidable delays by defining the scope early and identifying the systems, services, data flows, and relevant Trust Services Criteria.
Assigning control owners helps ensure that each activity has a responsible person and a clear follow-up process. Existing policies should also be reviewed to confirm that the documentation reflects actual business practices.
A readiness assessment can help prioritize gaps according to risk, customer commitments, and remediation effort. Maintaining accessible, dated evidence makes it easier to demonstrate control operation and identify missing records.
Technical weaknesses should be addressed promptly, with corrective actions documented. Early coordination with the independent service auditor can also clarify scope and examination expectations. Suitable automation tools may further improve task tracking and evidence organization.
These activities can make preparation more efficient, but they cannot eliminate the need for control operations, testing, or independent examination.
The SOC 2 timeline depends on existing security maturity, the selected report type, infrastructure complexity, systems and third-party services in scope, evidence quality, remediation requirements, internal team responsiveness, and auditor availability.
A business with established controls and consistent records may progress faster than an organization building its compliance program from the beginning.
SOC 2 Type 2 also requires an agreed observation period during which the auditor evaluates whether relevant controls operate effectively. Depending on control maturity and the engagement plan, some readiness activities may take place before or alongside this period.
No single timeline applies to every company. A reliable plan identifies dependencies and sets realistic milestones rather than guaranteeing a report date.
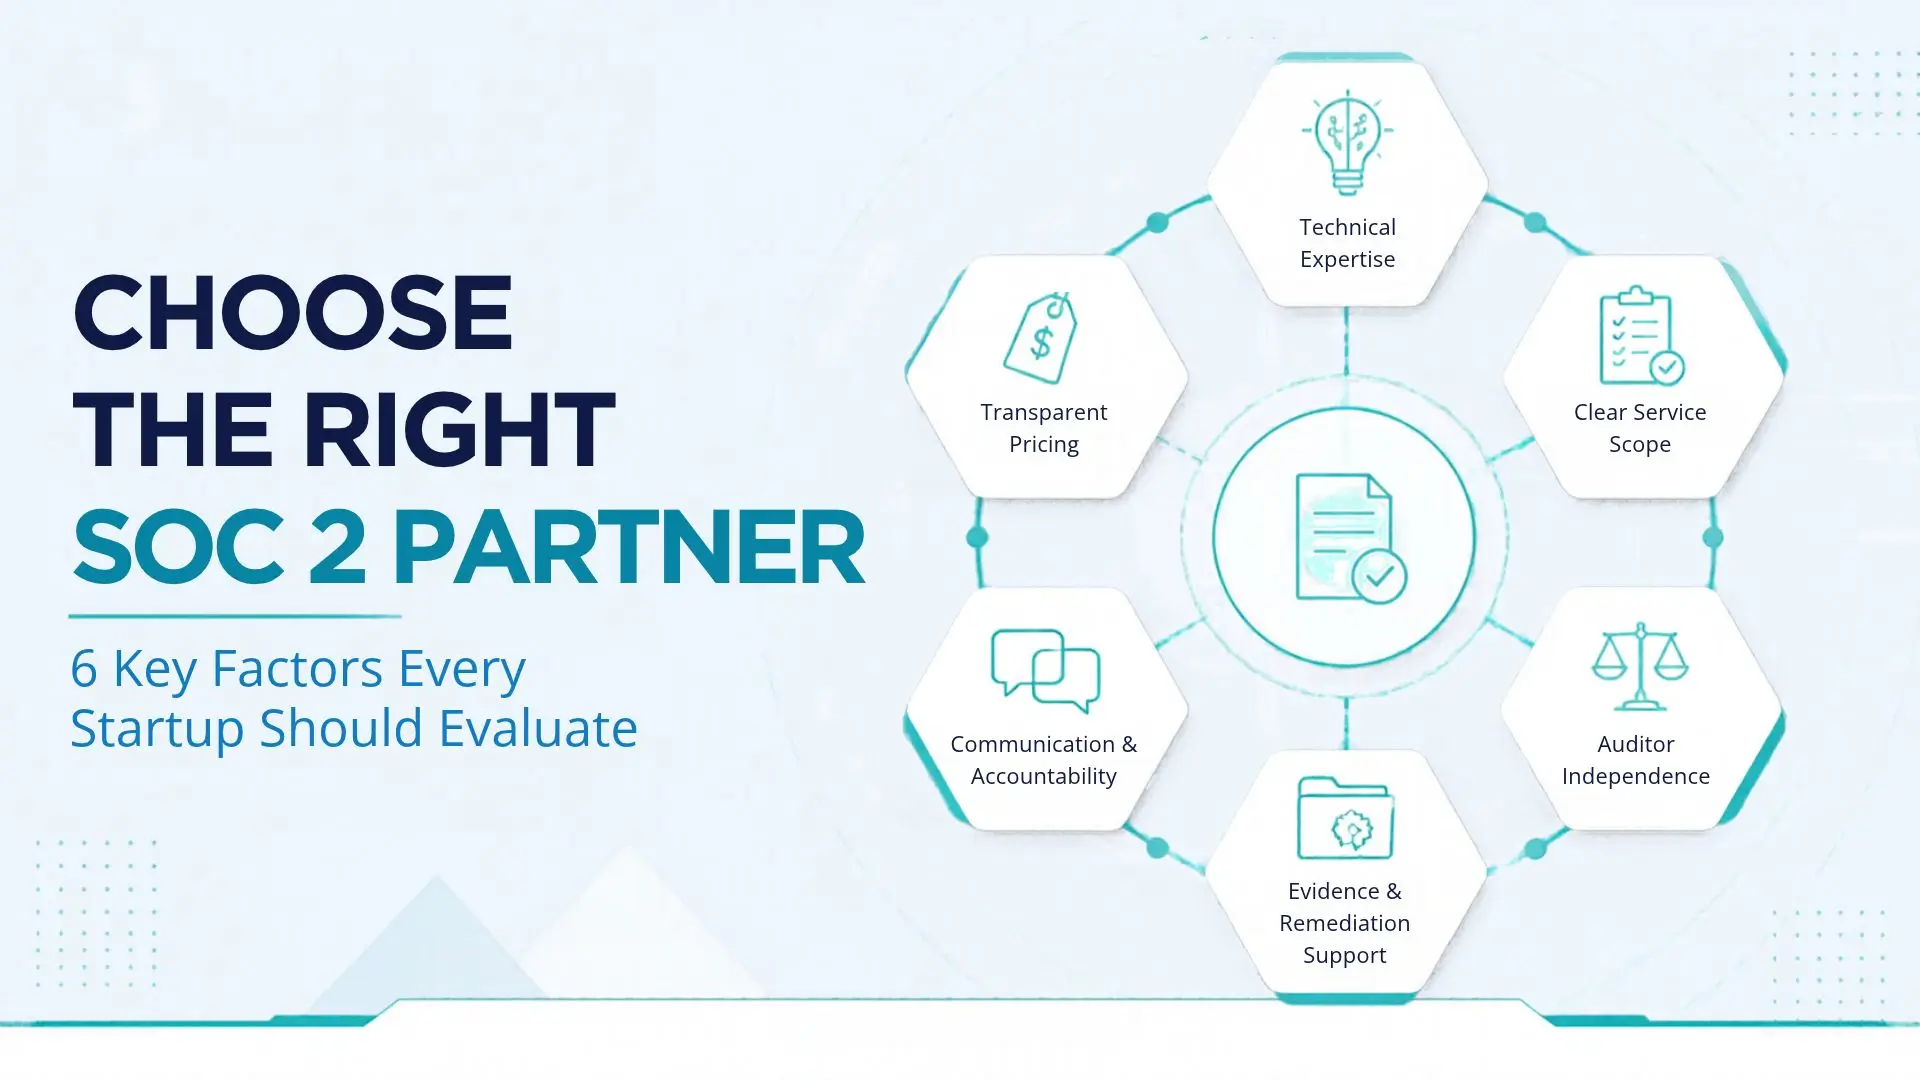
Look for relevant experience with SaaS, fintech, cloud, and technology businesses. Ask the provider to explain the difference between SOC 2 readiness consulting and independent auditing, including who will perform each role.
Request transparent information about scope, fees, deliverables, responsibilities, and realistic milestones. Structured gap assessments, remediation guidance, evidence organization, and regular progress updates are also important when evaluating readiness support.
Be cautious of guaranteed reports or unusually short timelines offered before anyone reviews your existing controls or accounts for the examination period. A reliable provider explains which activities can be accelerated and which requirements must still be completed.
Before choosing a provider, discuss your customer deadline, systems in scope, current policies, evidence sources, and unresolved technical issues. Request a written plan that separates readiness activities from independent examination milestones. This makes it easier to compare proposals and understand the responsibilities of your internal team.
Aanetic provides cybersecurity and compliance support to businesses preparing for SOC 2. Its readiness support can help organizations identify control gaps, improve documentation, organize evidence, and coordinate preparation activities before the independent examination.
Business-Specific Planning: Preparation should reflect your systems, customer requirements, security practices, and business risks.
Clear Gap Prioritization: Identifying gaps helps teams understand which improvements need attention and assign responsibilities.
Practical Evidence Guidance: Organized records make it easier to identify missing information and demonstrate how controls operate.
Support for Technology Teams: Clear responsibilities help startups coordinate compliance activities alongside their regular product and business operations.
Transparent Next Steps: Aanetic can help businesses discuss their current position and identify practical readiness activities.
SOC 2 readiness support does not constitute a completed examination or guarantee a report. The independent service auditor examines the relevant controls and issues the report.
Businesses can make their SOC 2 journey more efficient by preparing evidence early, assigning clear responsibilities, and addressing control gaps promptly. However, faster preparation should never compromise the effectiveness of control or independent examination.
Looking to streamline your SOC 2 journey? Contact Aanetic to discuss your SOC 2 readiness requirements, assess outstanding gaps, and plan practical next steps for your organization
Define the scope early, assign control owners, assess gaps, address weaknesses promptly, and maintain organized evidence. Coordinate with the relevant professionals to understand examination expectations and dependencies.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
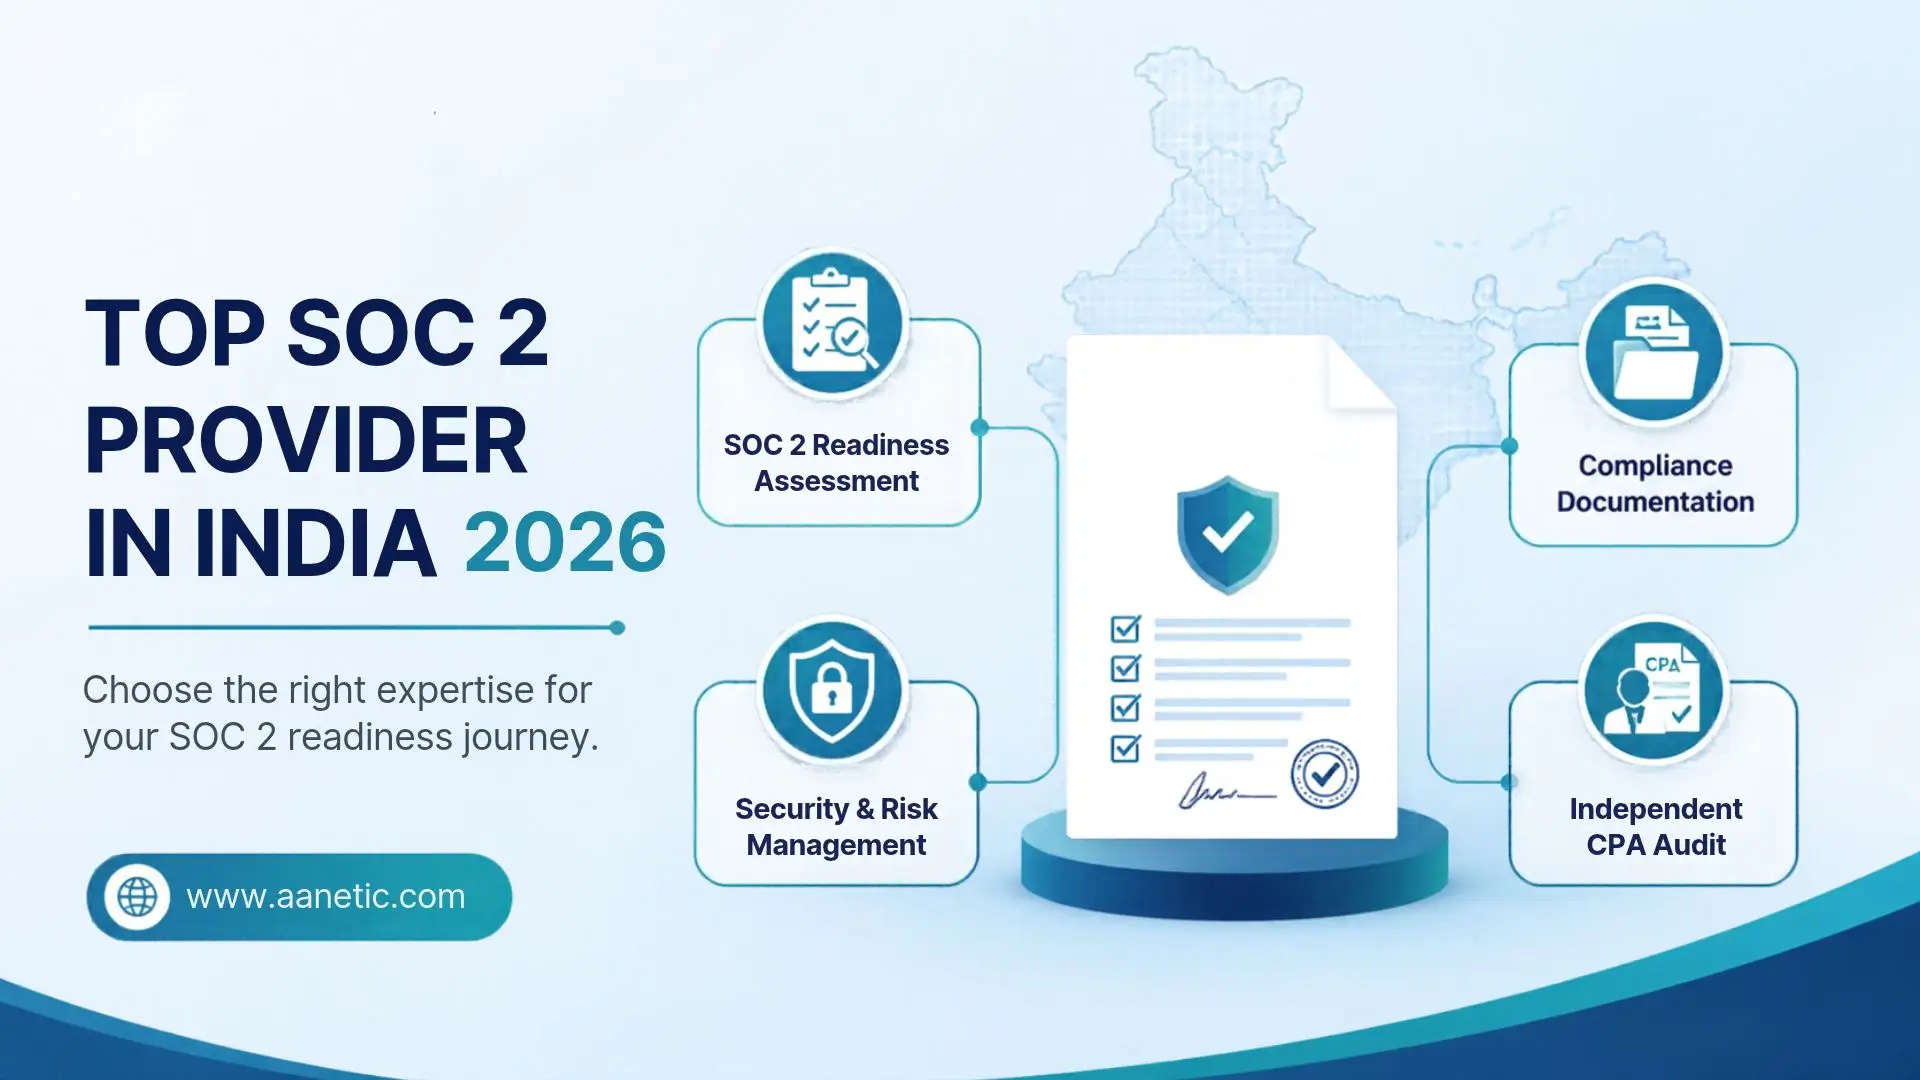
Looking for the top SOC 2 certification provider in India in 2026? Learn how Aanetic streamlines SOC 2 Type 1 and Type 2 readiness and audit support for SaaS.
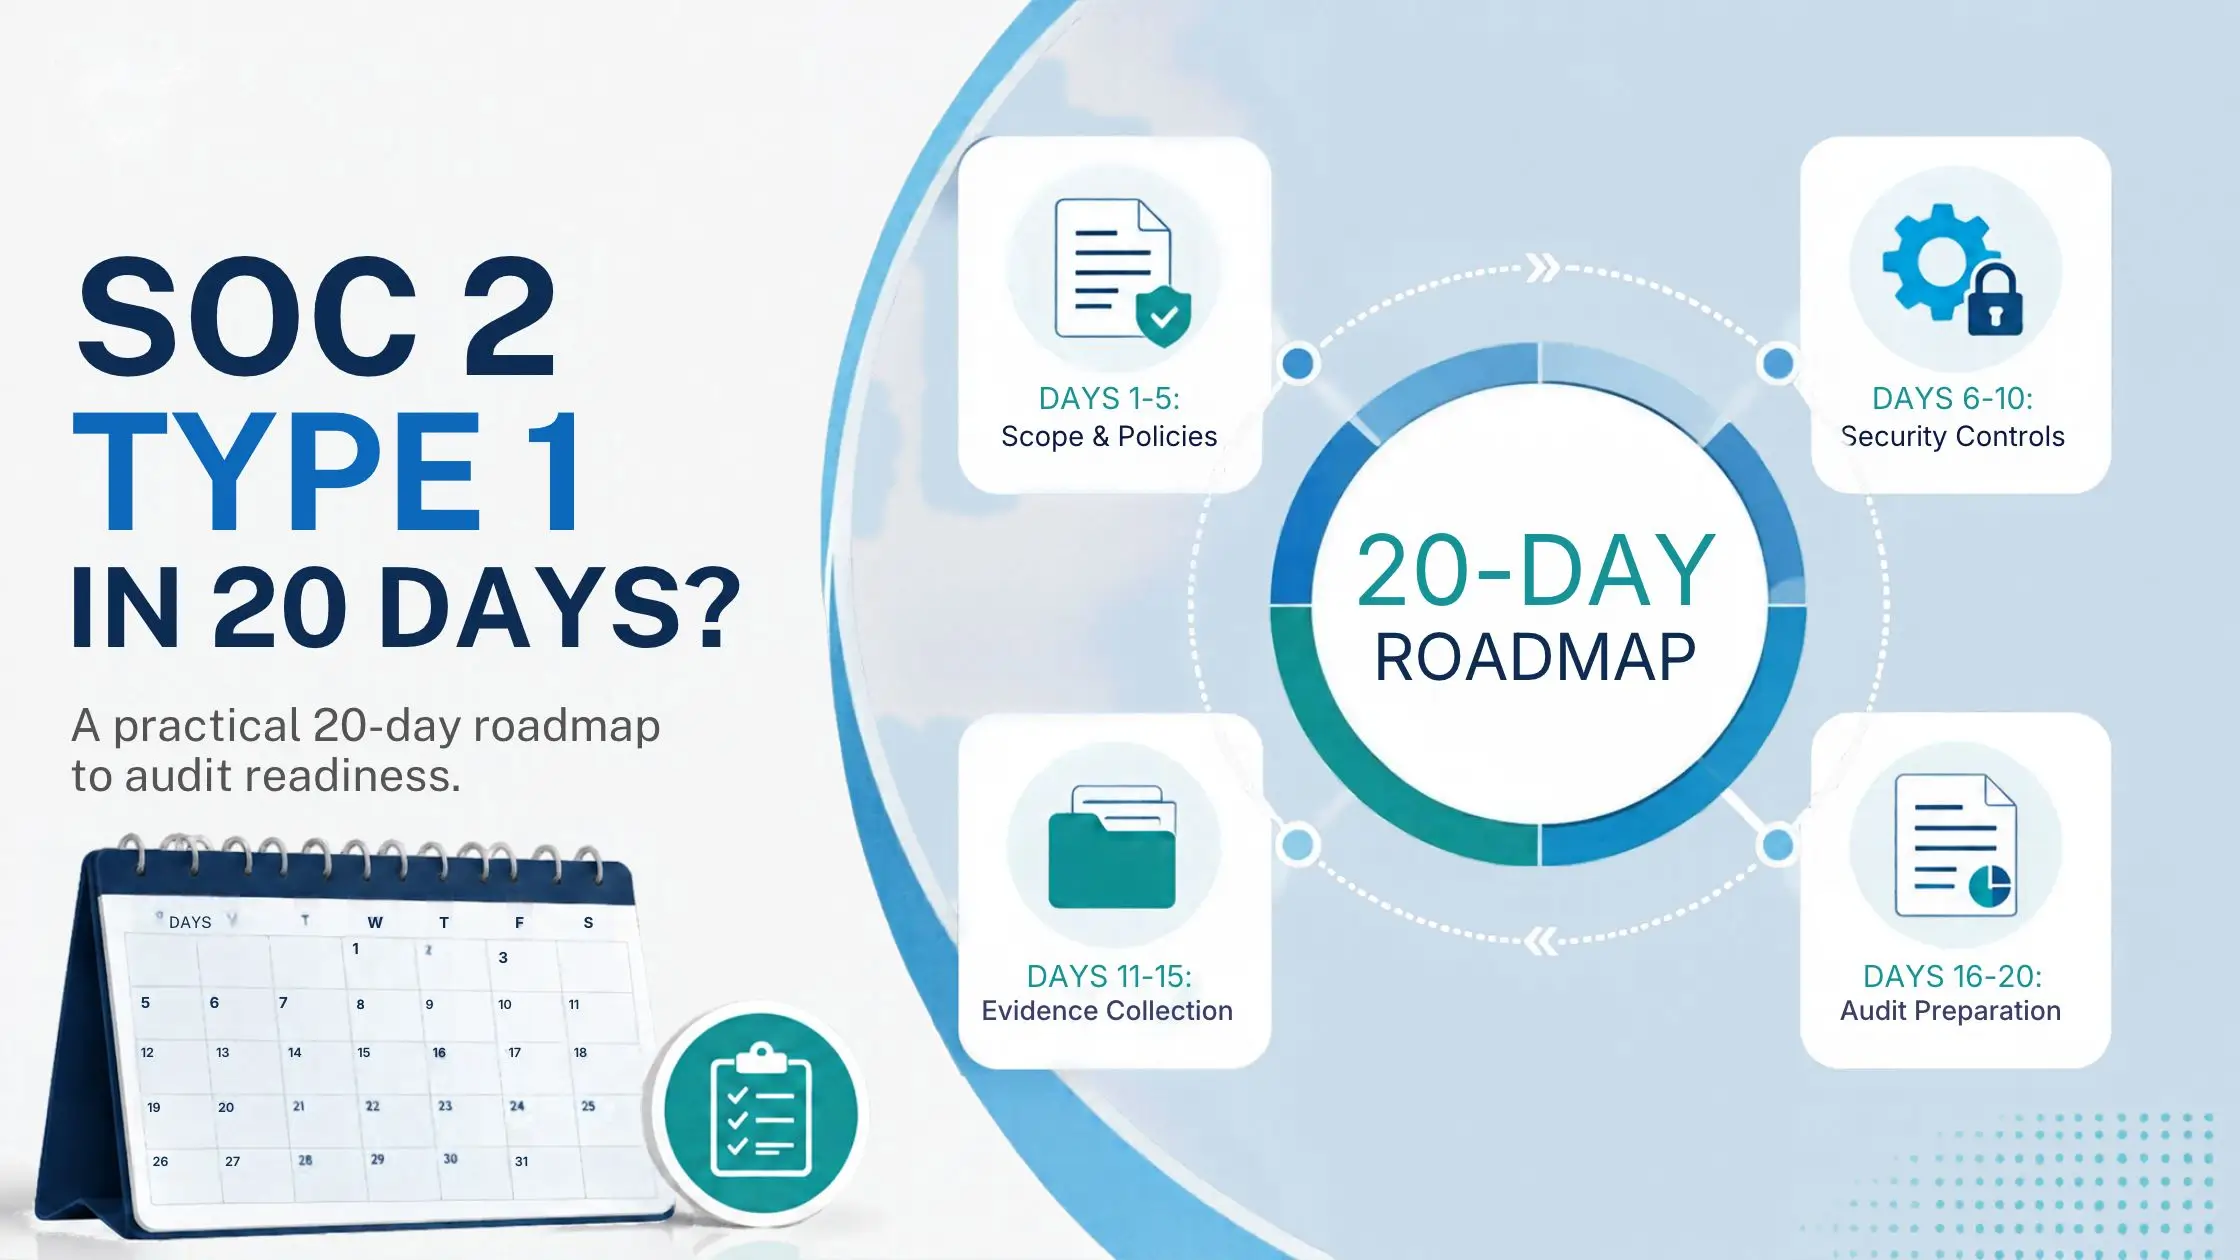
Fast-track your SOC 2 Type 1 audit readiness in 20 days. Learn how Aanetic streamlines scoping, policies, and technical evidence to unblock enterprise sales.
Get fast, budget-friendly SOC 2 compliance for your startup. Streamline gap analysis, automate evidence collection, and pass your audit with Aanetic.