26 October 2026
|6:34 pm
|Aanetic Advisory Editorial
Learn how to fast-track SOC 2 Type 2 with efficient readiness planning, compliance automation, evidence collection, and Aanetic's technology-enabled approach.
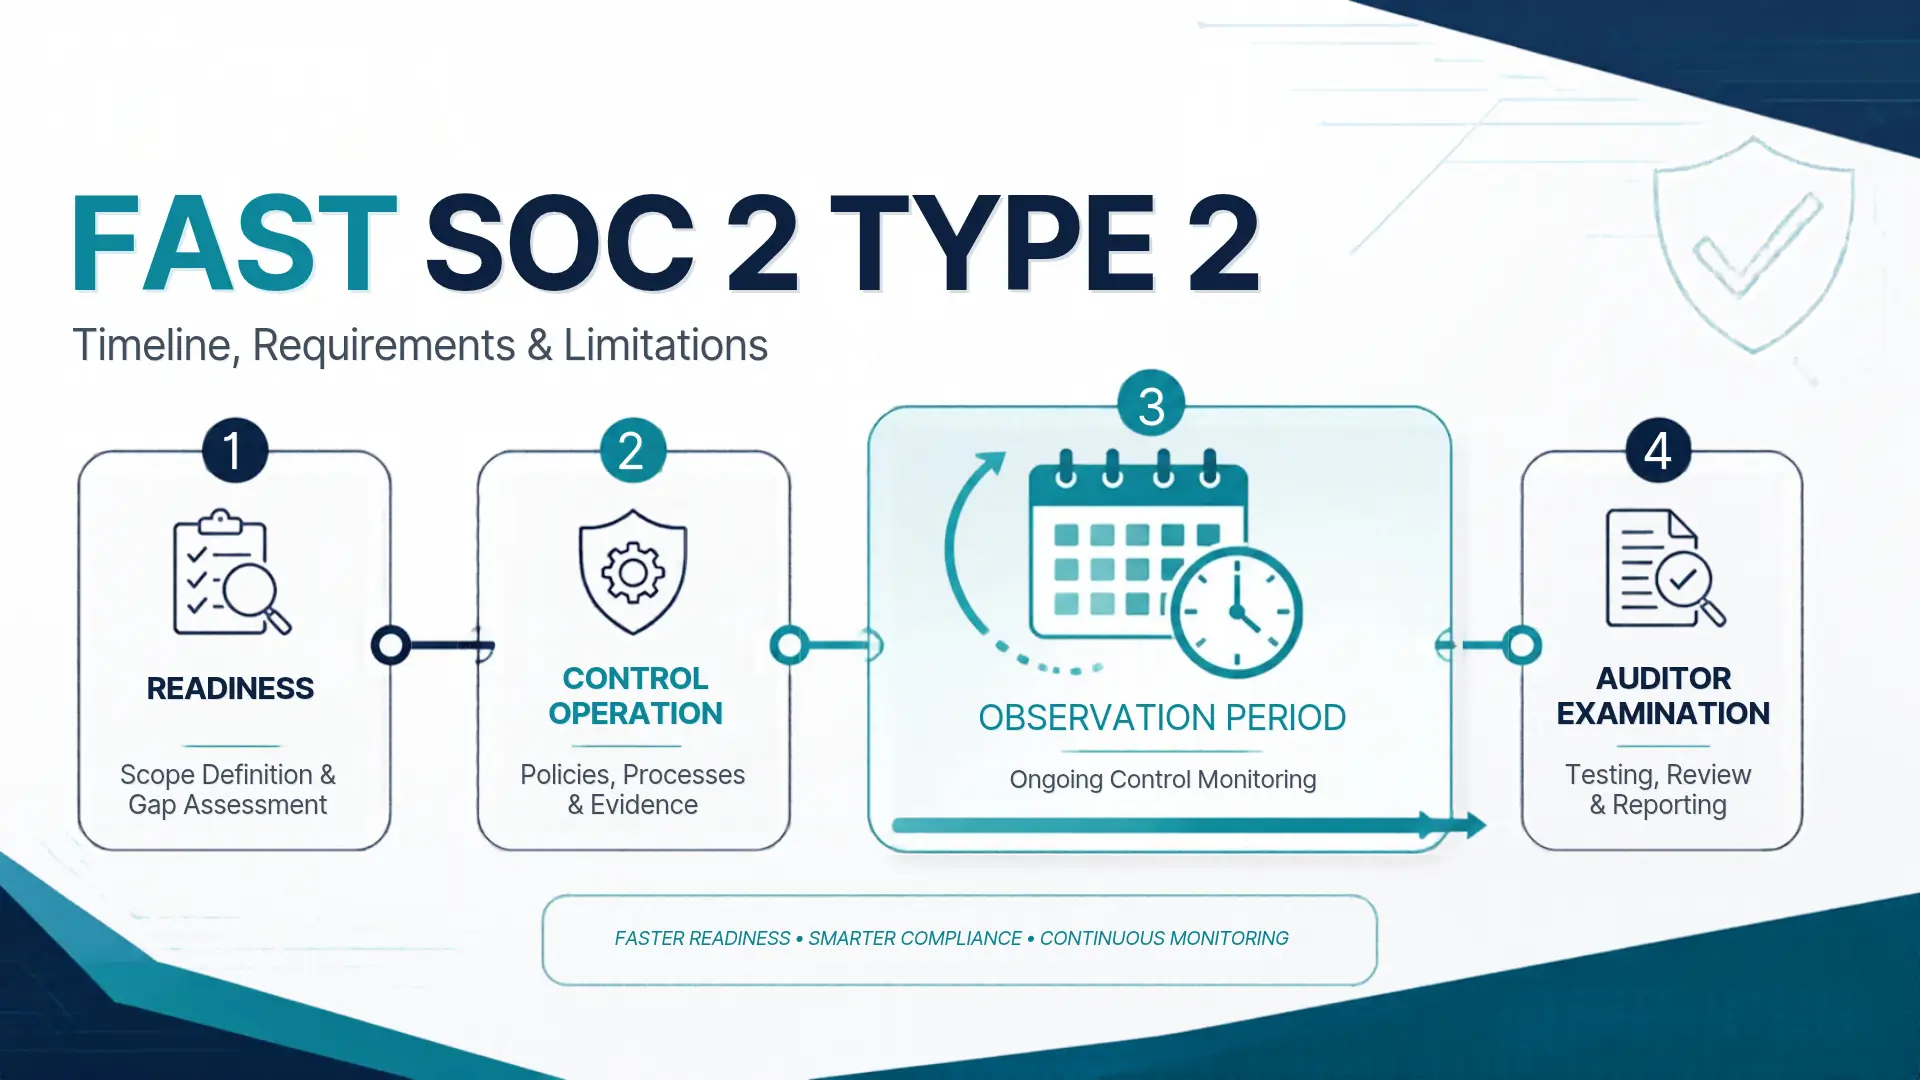
Enterprise sales cycles often slow down during vendor security reviews. When procurement teams request third-party assurance, a self-assessment is not enough. They expect an independent CPA-backed attestation. For SaaS providers, cloud platforms, and data processors, understanding how to fast-track SOC 2 Type 2 is essential. You should realistically assess timelines, requirements, and limitations to keep deals moving and maintain strong audit integrity.
Traditional compliance can take 9 to 12 months, but Aanetic speeds up readiness, gap remediation, and evidence collection in just a few weeks. This helps your systems become audit-ready and pass CPA review without delays.
The American Institute of Certified Public Accountants (AICPA) governs SOC 2 reporting under SSAE 18 attestation standards.
SOC 2 Type 1: Evaluates whether security controls are suitably designed at a single point in time.
SOC 2 Type 2: Assesses the operational effectiveness of those controls over an extended observation window (typically 3, 6, or 12 months).
Traditional consulting models drag this process out for a year due to manual document tracking, slow ticketing handoffs, and trial-and-error policy writing. With modern engineering workflows, the preparatory phase requires no more than a few focused weeks.
Accelerating SOC 2 Type 2 relies on eliminating organizational latency between discovery, engineering fixes, and CPA evidence requests.
Phase | Traditional Manual Process | Aanetic Fast-Track Acceleration | Core Milestones |
Scoping & Gap Analysis | 4 to 6 weeks | Under 1 week | Identifying cloud perimeter, code repos, and applicable Trust Services Criteria. |
Technical Remediation & Policies | 8 to 12 weeks | 1 to 2 weeks | Rapid deployment of MFA, RBAC, branch protection, CI/CD gates, and audit-ready policies. |
Observation Window | 6 to 12 months | 3 months (Minimum CPA Floor) | Real-time continuous evidence gathering with zero control drift. |
CPA Audit & Report Delivery | 6 to 8 weeks | 1 to 2 weeks | Pre-packaged auditor dossiers, eliminating back-and-forth query cycles. |
To move from zero to audit readiness in weeks, foundational technical and operational controls must be implemented immediately:
Delays occur when teams review systems that neither process nor store customer data. Aanetic focuses on production boundaries and begins with the Security Criteria (Common Criteria), adding Availability or Confidentiality only if enterprise customer agreements require it.
Identity & Access Management: Enforce hardware/app-based MFA and Role-Based Access Control (RBAC) across AWS, GCP, GitHub, and production databases within days.
Automated Change Management: Configure branch protection rules that require mandatory code reviews, passing unit tests, and blocking direct pushes to production branches.
Data Encryption Standards: Implement TLS 1.3 in transit and AES-256 at rest across all storage buckets, RDS instances, and backups.
Vulnerability Management & VAPT: Complete a targeted Vulnerability Assessment and Penetration Testing run, fixing critical and high-severity findings before commencing observation.
Auditors scrutinize HR and identity terminations. Implement clear, logged access-revocation steps so that team members who leave lose system access within 24 hours.
Even if you complete onboarding and remediation in just a few weeks, some regulatory requirements cannot be changed:
The 3-Month Minimum Observation Floor: While Aanetic completes scoping, gap-fixing, and readiness in just a few weeks, CPAs require at least 3 months of operational history to attest to the effectiveness of controls over time.
Zero retroactive fixing: If a control fails during the observation window, such as an unreviewed PR or an unrevoked user account, it is flagged as an exception. Continuous monitoring ensures these failures do not invalidate the observation period.
Independent CPA Attestation: Only licensed, independent CPA firms can sign off on SSAE 18 attestation reports; advisory teams structure and execute the technical readiness to ensure the CPA issues a clean report.
Aanetic Technology eliminates manual work that slows SOC 2 compliance. Instead of giving you endless spreadsheets, Aanetic works directly with your engineering team to deliver fast, concrete results:
Direct Hands-On Remediation: Aanetic works alongside engineering and DevOps teams to configure cloud permissions, logging policies, and code branch safeguards, cutting weeks of guesswork into days of direct implementation.
Automated Compliance Architecture: Aanetic hooks directly into your cloud stack (AWS, Azure, GCP, GitHub, Google Workspace) to establish continuous evidence collection and alert your team the moment a control drifts.
CPA-Ready Audit Dossiers: Aanetic formats policies, vendor risk assessments, and infrastructure configurations directly to CPA standards, cutting audit fieldwork down to days instead of months.
Cross-Framework Efficiency: Readily map SOC 2 controls to the DPDP Act, ISO 27001, or GDPR to prevent redundant compliance workflows down the line.
Less manual effort: Streamlined evidence collection and organized workflows.
Better visibility: Clearer oversight of control status, remediation tasks, and outstanding evidence.
Faster gap resolution: Prioritized remediation helps teams focus on important compliance requirements.
Improved coordination: Defined responsibilities help reduce missed tasks and duplicated work.
Ongoing readiness: Continuous monitoring supports consistent control operation and future compliance activities.
The actual timeline will depend on the organization's existing control maturity, the scope of the examination, and the agreed examination period. Aanetic's approach is to improve readiness efficiency whilst still meeting the evidence and control requirements for a credible SOC 2 Type 2.
Enterprise revenue shouldn't be held up by slow compliance cycles. How do you accelerate your SOC 2 Type 2? The timelines, requirements, and limitations are all easily addressed when you've got actual engineering specialists on the ground leading the process.
Partner with Aanetic Technology to complete your SOC 2 readiness in weeks, streamline CPA testing, and close enterprise deals with confidence.
Aanetic handles gap remediation, policy automation, and technical controls in just 2 to 3 weeks. After that, your team can start the formal observation period right away.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
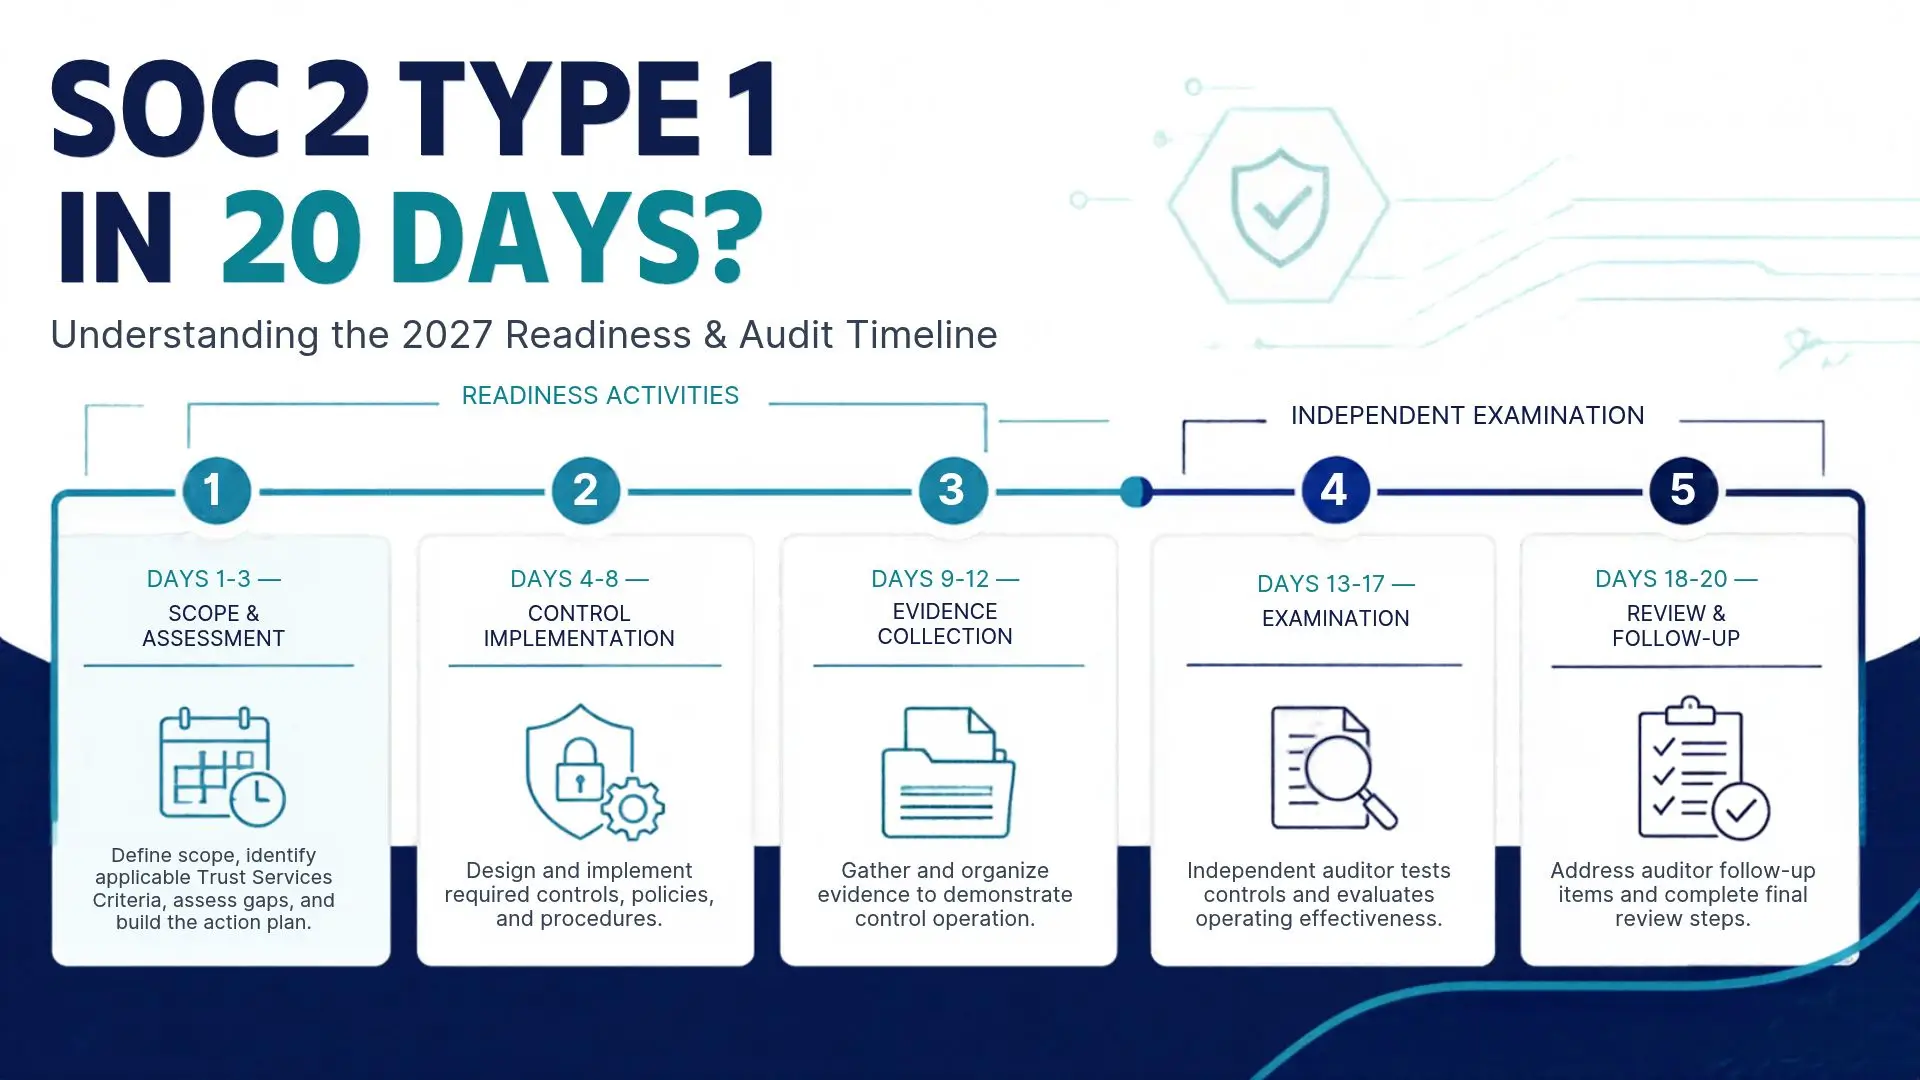
Fast-track SOC 1 and SOC 2 readiness for 2027 with Aanetic. Identify compliance gaps, improve controls, organize evidence, and prepare for an independent audit.
Learn how to choose right partners for your SOC 2 audit. Discover key criteria, Type 1 vs Type 2 scoping, and why Aanetic is India’s top GRC compliance advisor.
Looking for the best DPDP Act consultant in India? Compare top advisory firms for consent architecture, DPIA audits, and DPO services to stay compliant.