2 November 2026
|10:14 am
|Aanetic Advisory Editorial
Looking for the top SOC 2 certification provider in India in 2026? Learn how Aanetic streamlines SOC 2 Type 1 and Type 2 readiness and audit support for SaaS.
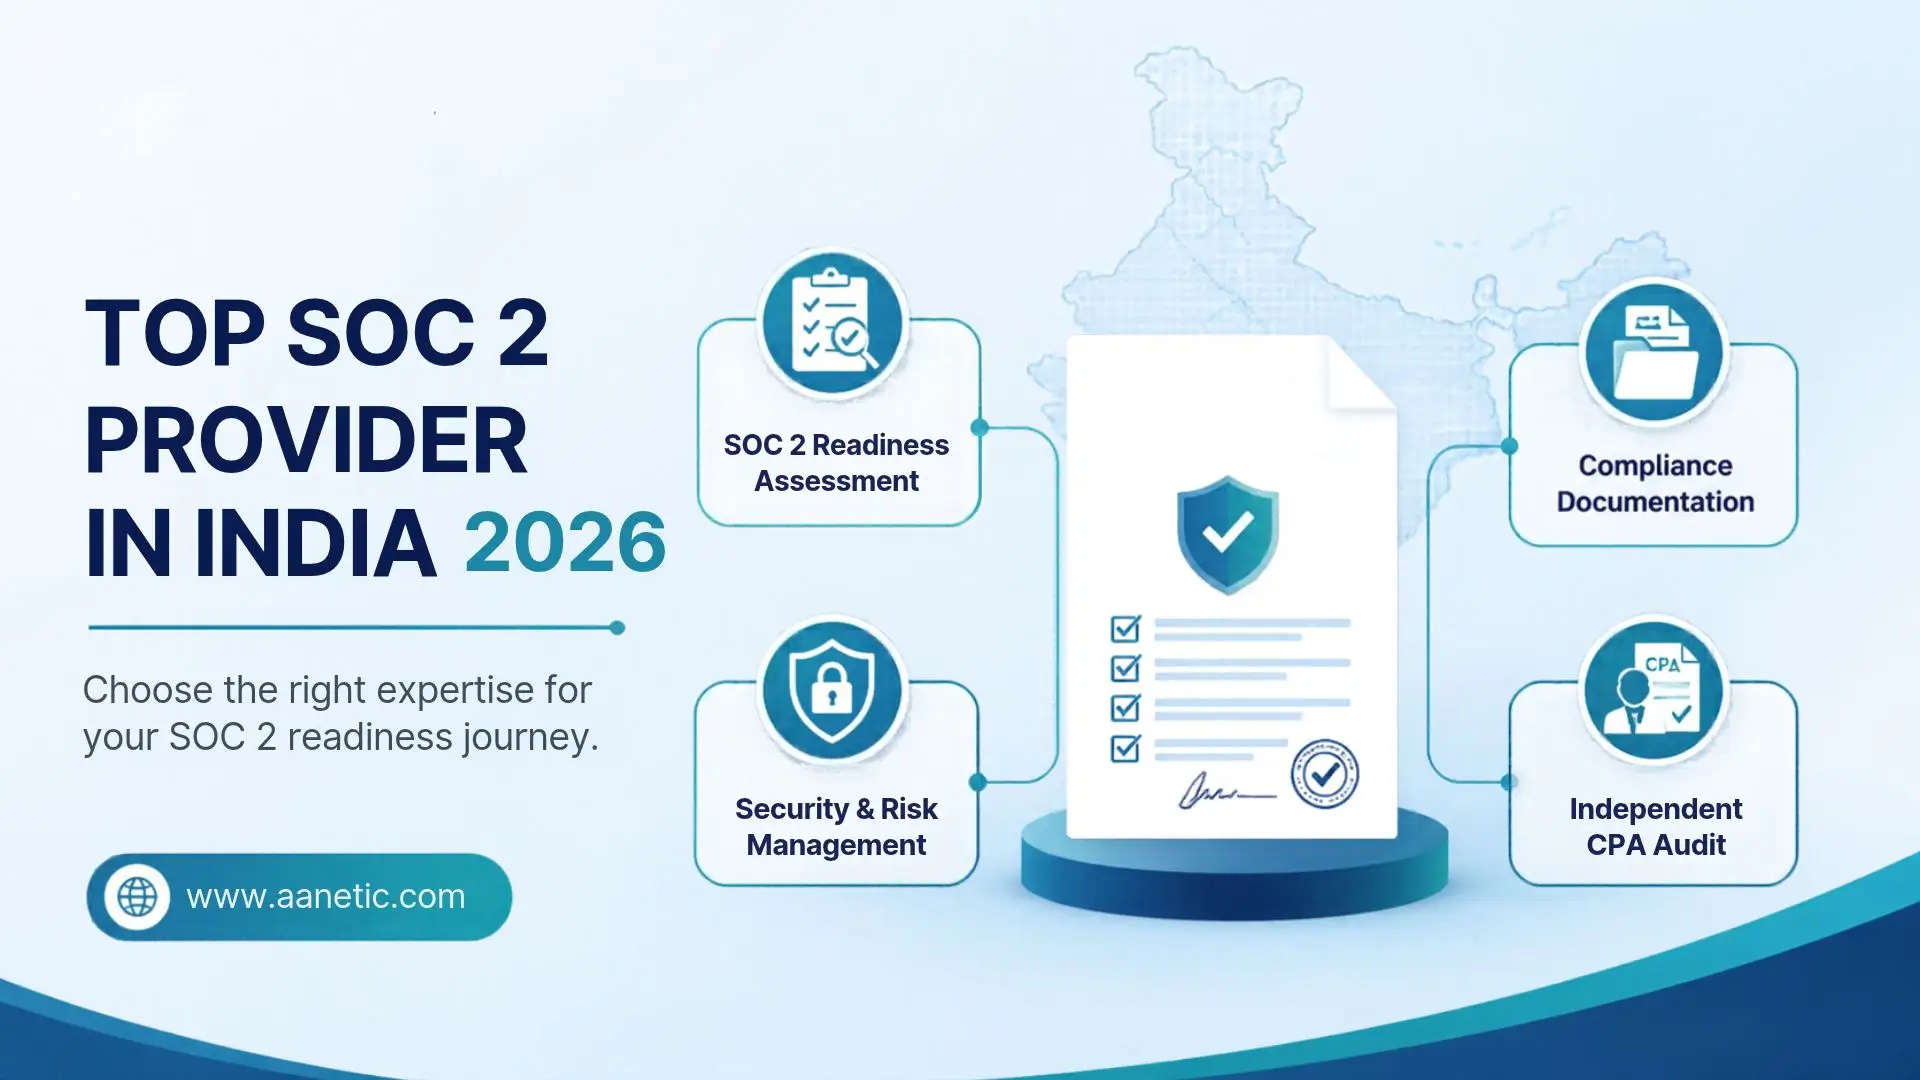
In 2026, data security and cloud compliance are no longer optional checkpoints—they are decisive revenue drivers for growing businesses. Whether expanding into the North American market, pitching Fortune 500 enterprises, or fielding stringent vendor security questionnaires, proving your security posture is essential.
Choosing the right partner can make all the difference. If you're in the process of evaluating the Top SOC 2 Certification Provider in India 2026, then this guide will go through the fundamentals of the compliance requirements, the practical steps you need to take to get ready, and how working with a modern compliance advisory leader (like Aanetic) can help your organization to get through the audit process with ease.
Developed by the American Institute of Certified Public Accountants (AICPA), a System and Organization Controls (SOC) 2 report evaluates how well a service organization protects sensitive customer data in the cloud. Unlike standard checklist certifications, SOC 2 focuses on evaluating internal control environments based on five fundamental Trust Services Criteria (TSC):
Security (Common Criteria): Protects information and systems against unauthorized access, unauthorized disclosure, and system damage. (Mandatory for all reports)
Availability: Verifies that systems and services maintain operational uptime and performance standards agreed upon in service level agreements (SLAs).
Confidentiality: Ensures that sensitive business information, intellectual property, and proprietary data remain restricted to authorized personnel.
Processing Integrity: Confirms that cloud system processing is complete, valid, accurate, timely, and authorized.
Privacy: Addresses the collection, use, retention, disclosure, and disposal of personal information in accordance with organization privacy notices.
When planning your compliance roadmap, selecting the correct report structure ensures your efforts match client expectations:
SOC 2 Type 1: Evaluates the design suitability of your security controls at a single point in time. It is ideal for startups and early-stage SaaS firms that need to build credibility quickly in the market to unblock enterprise deals.
SOC 2 Type 2: Evaluates both the design and operational effectiveness of controls over an extended review window (typically 3, 6, or 12 months). It represents the industry benchmark that mature procurement teams require to verify ongoing operational discipline.
India has cemented its reputation as a global hub for SaaS, outsourced technology services, and cloud engineering. As global buyers raise the bar on third-party vendor risk management, international clients expect robust third-party security validations before signing contracts.
Shortened Enterprise Sales Cycles: A recognized SOC 2 report resolves lengthy vendor risk assessment questionnaires, enabling sales teams to close cross-border enterprise contracts faster.
Global Market Alignment: SOC 2 provides international parity with domestic frameworks, including the Digital Personal Data Protection (DPDP) Act and ISO/IEC 27001.
Structured Cloud Risk Governance: Documenting access controls, continuous monitoring, and disaster recovery strategies reinforces engineering resilience against emerging cyber threats.
SOC 2 reports are formally issued by an independent, licensed CPA firm under the AICPA SSAE 18 attestation standards. The real hard bit of compliance is the preparation phase, though: scoping the systems, writing the policies, implementing the technical controls, remediating vulnerabilities, and gathering audit-ready evidence.
When looking for the top SOC 2 advisory and readiness partner in India, evaluate firms across these critical dimensions:
Hands-On Readiness vs. Automated Checklists: Pure automation software tools often leave teams confused with dozens of red flags. The most effective partners blend structured workflows with dedicated guidance from cybersecurity consultants.
Tailored scoping and pragmatic controls: over-scoping the Trust Services criteria results in a massive increase in audit complexity with no commercial benefit. The experienced advisors will, of course, focus solely on the criteria relevant to your customer commitments.
End-to-End Remediation Support: Advisors should actively guide engineering teams through technical fixes—from AWS/Azure/GCP IAM configurations to Mobile Device Management (MDM) rollouts.
Smooth Audit Coordination: Top advisory providers manage the liaison with accredited CPA audit teams, minimizing confusion, handling evidence submissions, and streamlining auditor queries.
As modern Indian tech organizations look for reliable compliance strategies, Aanetic has positioned itself as a leader in cybersecurity, GRC, and compliance readiness. They bring the technical know-how to the table but also a business-centric approach that allows you to build a defensible security program without necessarily slowing down developer velocity.
Aanetic works directly with your technical and leadership teams to conduct architecture, cloud, and workflow analyses. The key thing it does is define the right boundary for your audit so you don't end up with unintended control creep.
Rather than handing teams generic, unmanageable policy templates, Aanetic helps implement customized, practical security procedures. From access control mechanisms and incident response plans to vendor risk management frameworks, controls are structured to reflect how your engineering team actually works.
Modern cloud environments require specialized technical hygiene. Aanetic’s specialists assist in aligning cloud controls across platforms such as AWS, Microsoft Azure, and Google Cloud Platform.
Least-privilege Identity and Access Management (IAM) and multi-factor authentication (MFA)
Infrastructure as Code (IaC) security and automated vulnerability patch tracking
End-to-end data encryption at rest and in transit
Continuous backup, disaster recovery, and failover verification
Navigating independent auditor inquiries can be daunting for internal teams. Aanetic organizes and validates your evidence repository before the audit engagement and assists your team throughout auditor review sessions to ensure that communications remain structured, clear, and efficient.
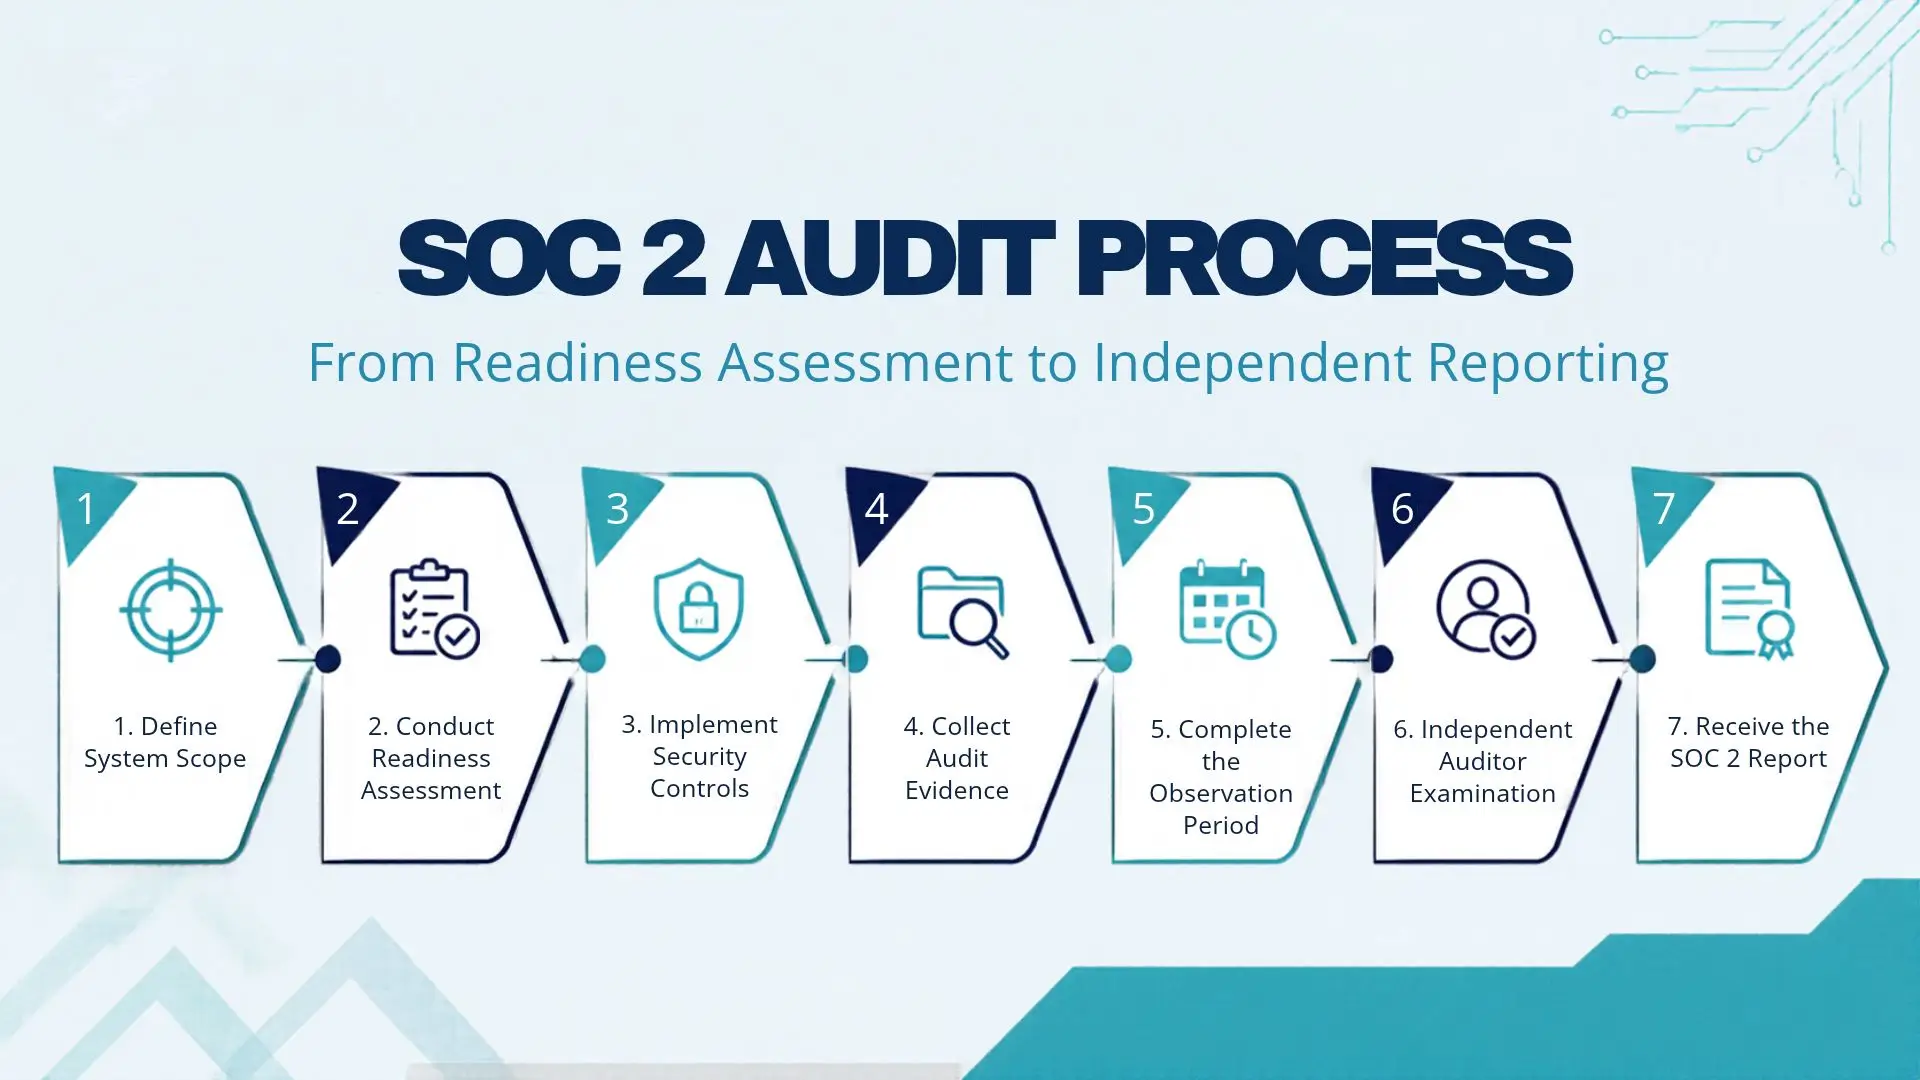
Scoping and Gap Analysis: Map out the system components (including people, data flows, and third-party tools) against the AICPA requirements to identify any missing operational controls.
Policy Formulation and Technical Remediation: Develop clear internal standards (e.g., Change Management, Business Continuity, HR Security) and configure technical safeguards across cloud environments.
Internal Readiness Evaluation: Conduct a simulated dry-run audit to ensure operational controls generate the exact documentation and system logs expected by reviewers.
Independent CPA Audit Engagement: Coordinate with an accredited CPA firm to conduct the formal SSAE 18 examination and evaluate control design (Type 1) or ongoing performance (Type 2).
Ongoing Governance and Renewal: Because Type 2 reports evaluate continuous adherence over time, maintaining daily operational controls ensures simple, predictable annual renewals.
Getting to SOC 2 attestation is a massive leap forward in terms of turning information security into a real competitive advantage. Working with a specialist, experienced advisor removes the element of guesswork, enables you to optimize your internal resources, and prepares your team for the audit.
If your organization is evaluating the Top SOC 2 Certification Provider in India 2026, connect with the specialists at Aanetic today to schedule an initial consultation and build a clear, audit-ready compliance roadmap.
According to AICPA guidelines, only an independent, licensed Certified Public Accountant (CPA) firm or an authorized CPA affiliate can issue an official SOC 2 report. Compliance advisory firms and security consultants help organizations prepare by assessing gaps, establishing controls, and gathering evidence before the independent auditor conducts the final audit.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
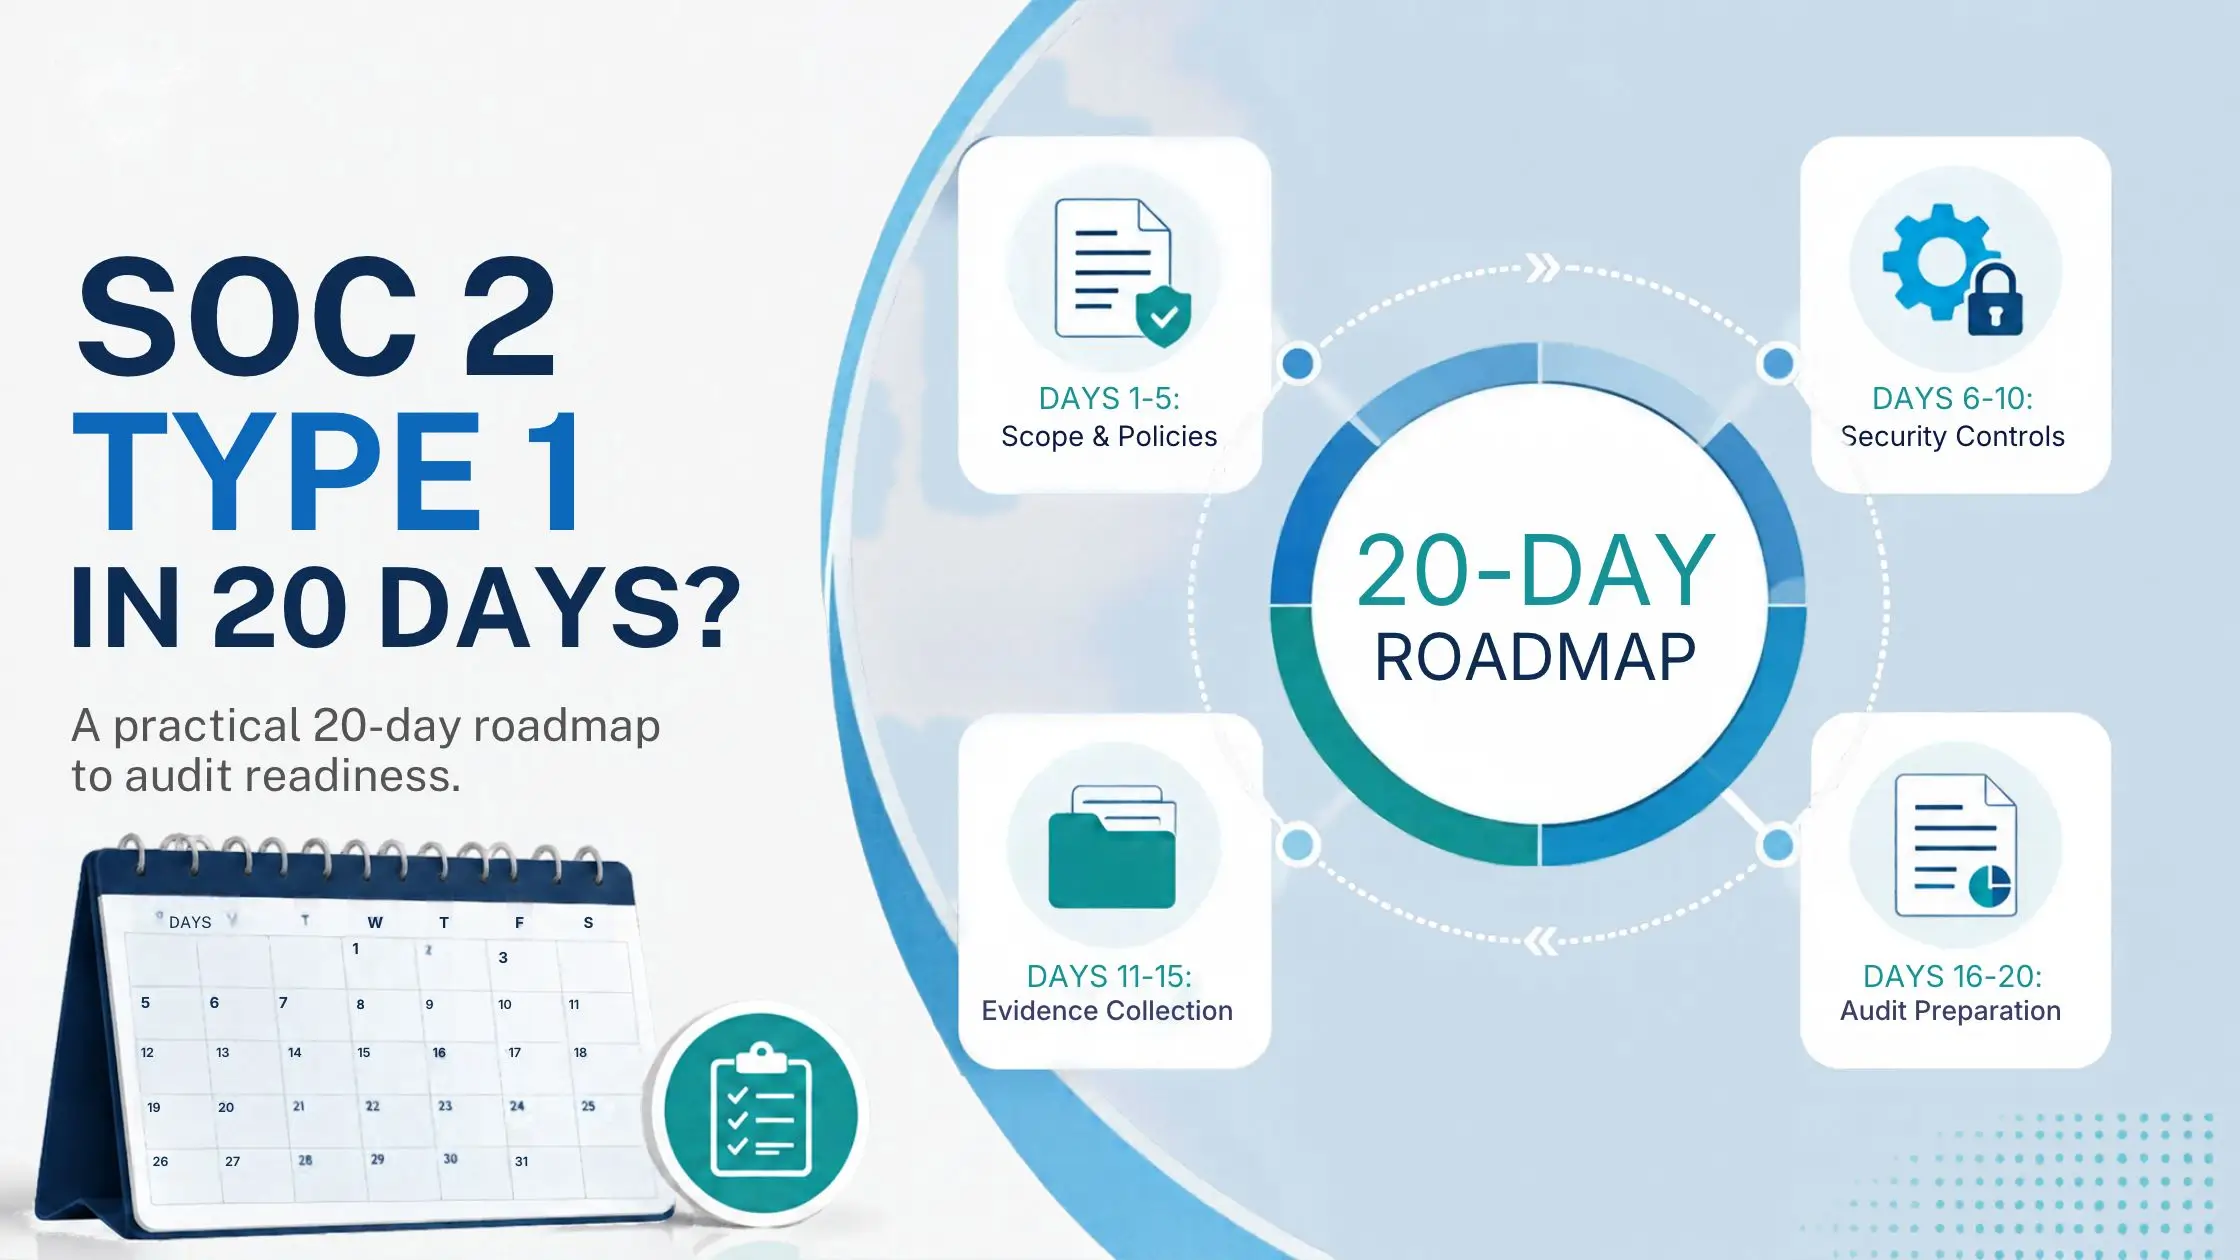
Fast-track your SOC 2 Type 1 audit readiness in 20 days. Learn how Aanetic streamlines scoping, policies, and technical evidence to unblock enterprise sales.
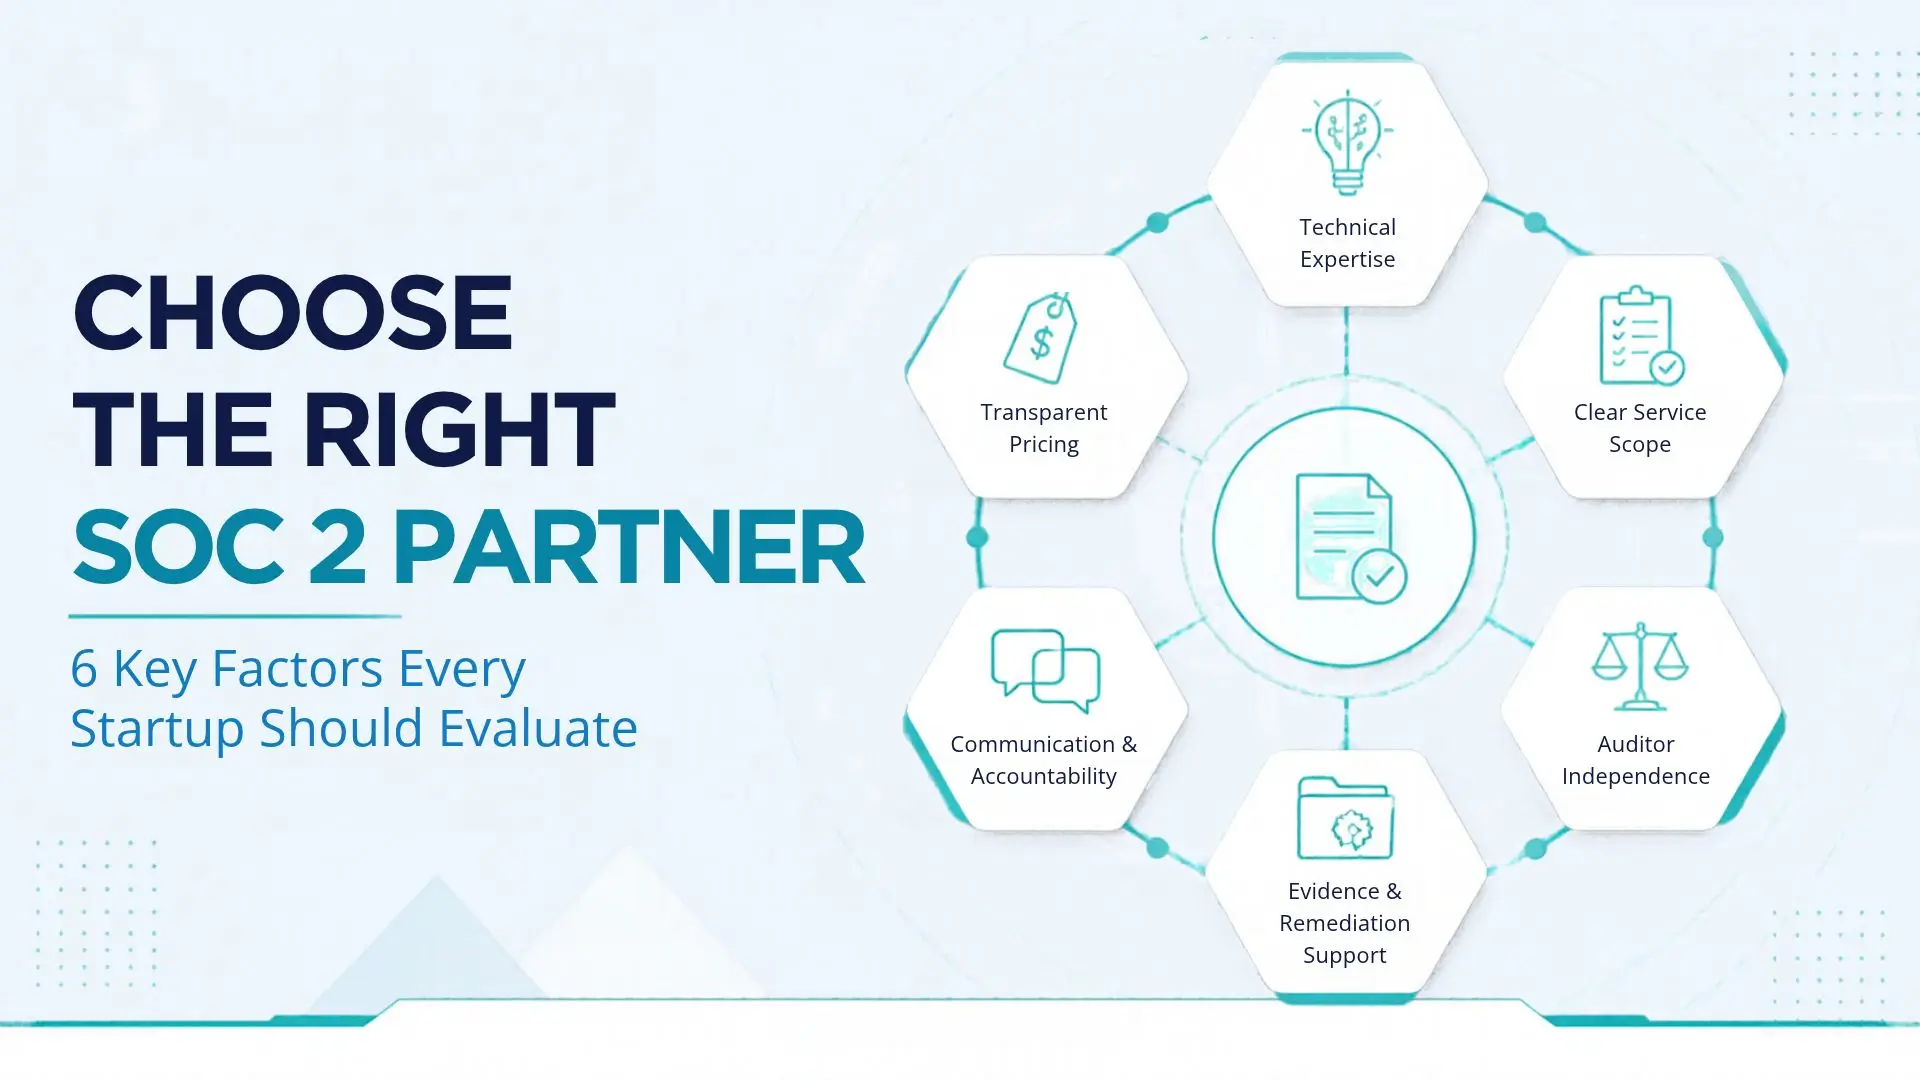
Get fast, budget-friendly SOC 2 compliance for your startup. Streamline gap analysis, automate evidence collection, and pass your audit with Aanetic.
Explore the top SOC 2 audit challenges for Indian startups, from scoping errors to access gaps, and see how Aanetic simplifies the pathway to attestation.