30 October 2026
|11:53 am
|Aanetic Advisory Editorial
Fast-track your SOC 2 Type 1 audit readiness in 20 days. Learn how Aanetic streamlines scoping, policies, and technical evidence to unblock enterprise sales.
To close enterprise SaaS deals, enter regulated markets, or pass tough vendor security reviews, you need clear proof of your data protection. Both fast-growing startups and established service providers now see SOC 2 audits as a basic requirement. Many organizations choose SOC 2 Type 1 readiness and compliance services with a 20-day preparation plan to help their teams align, establish strong processes, and prepare for assessment without slowing operations.
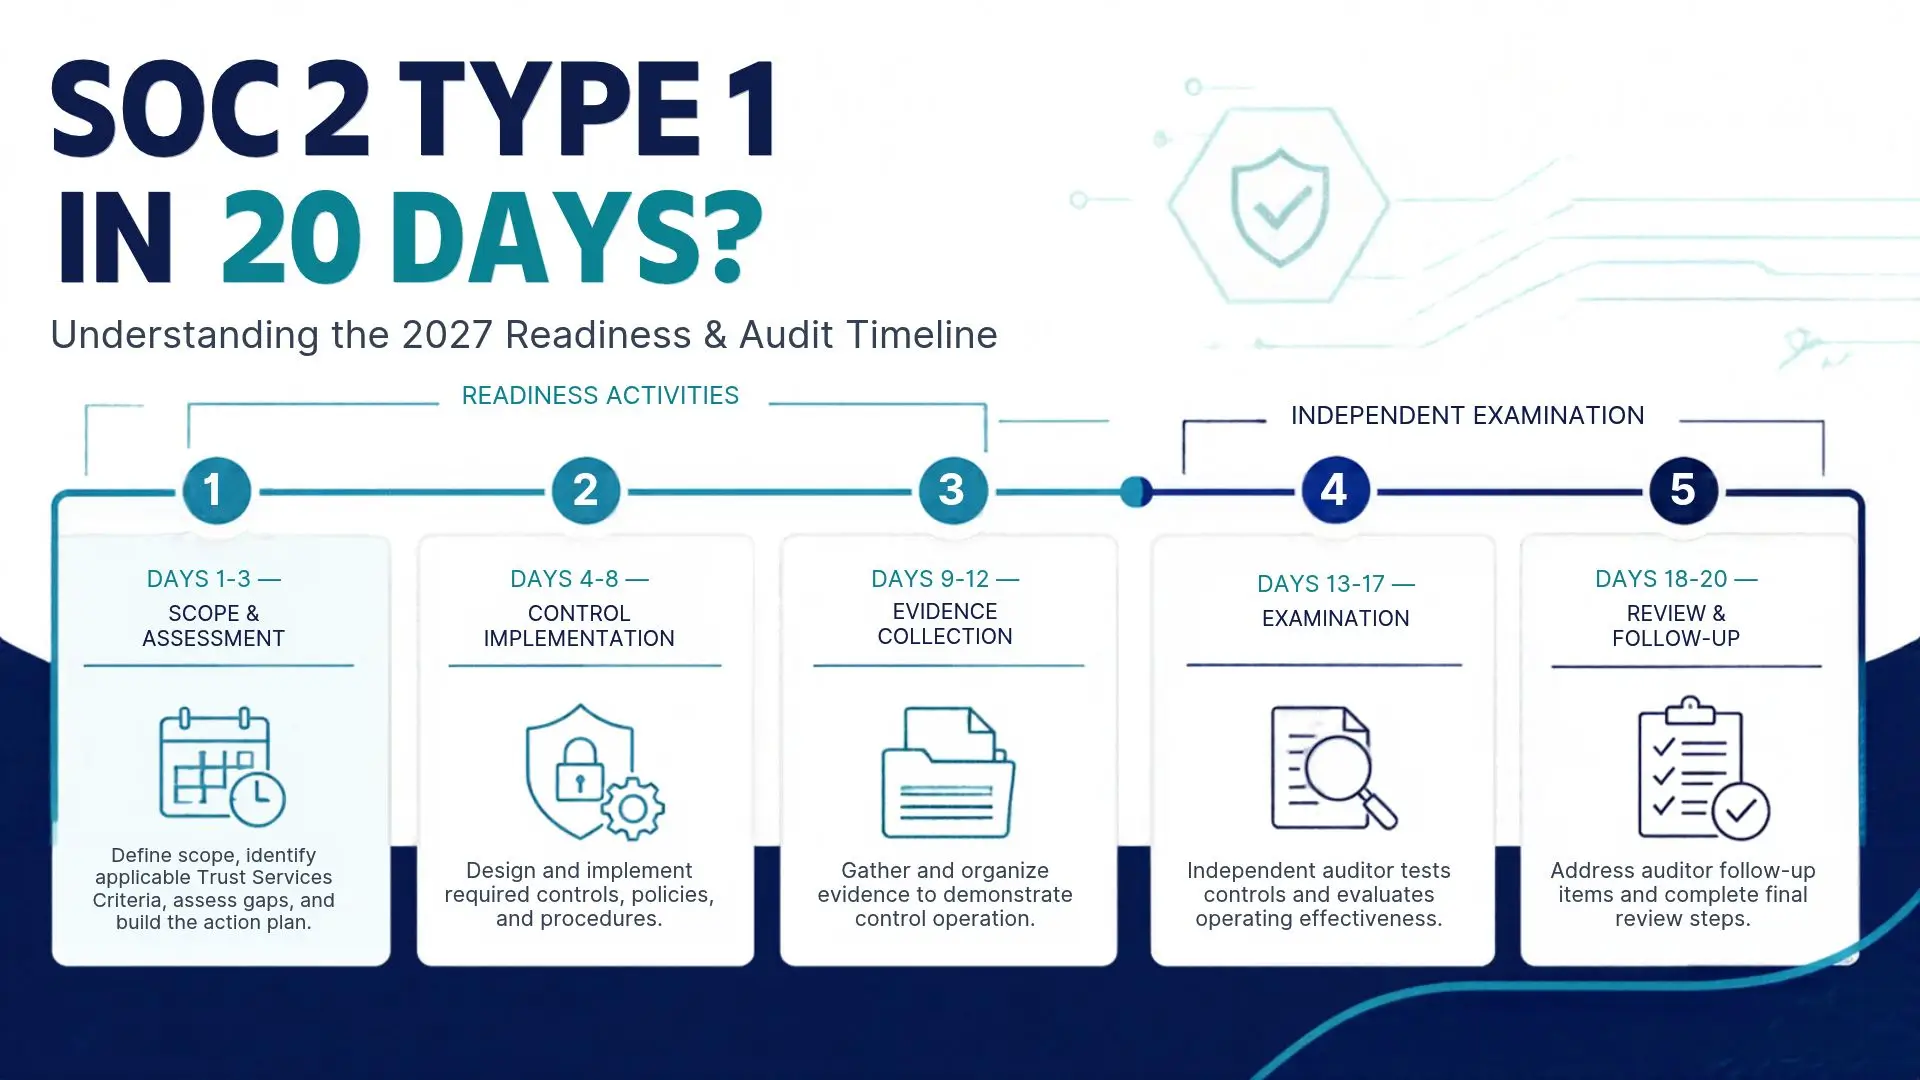
Working through the AICPA Trust Services Criteria doesn’t have to slow down your engineering team. With clear scoping, focused gap fixes, and help from compliance experts like Aanetic, your organization can get ready efficiently. Here’s a practical, day-by-day roadmap to take your team from the first assessment to audit-ready controls in 20 business days.
A SOC 2 Type 1 report assesses whether your security controls are configured to meet the AICPA Trust Services Criteria at a specific point in time. Unlike a Type 2 exam, which assesses how well controls work over 3 to 12 months, Type 1 focuses on whether your policies, system details, configurations, and technical controls are in place and working now.
By 2027, compliance will require greater precision due to more complex cloud setups, third-party APIs, and automated security pipelines. Getting ready early helps fast-moving teams to:
Validate foundational security architecture before locking in long-term control operations.
Provide enterprise procurement teams with credible, third-party-reviewed proof of security.
Identify control redundancies and configuration misalignments before engaging an independent CPA auditor.
Lay an organized foundation for transitioning into a SOC 2 Type 2 observation window.
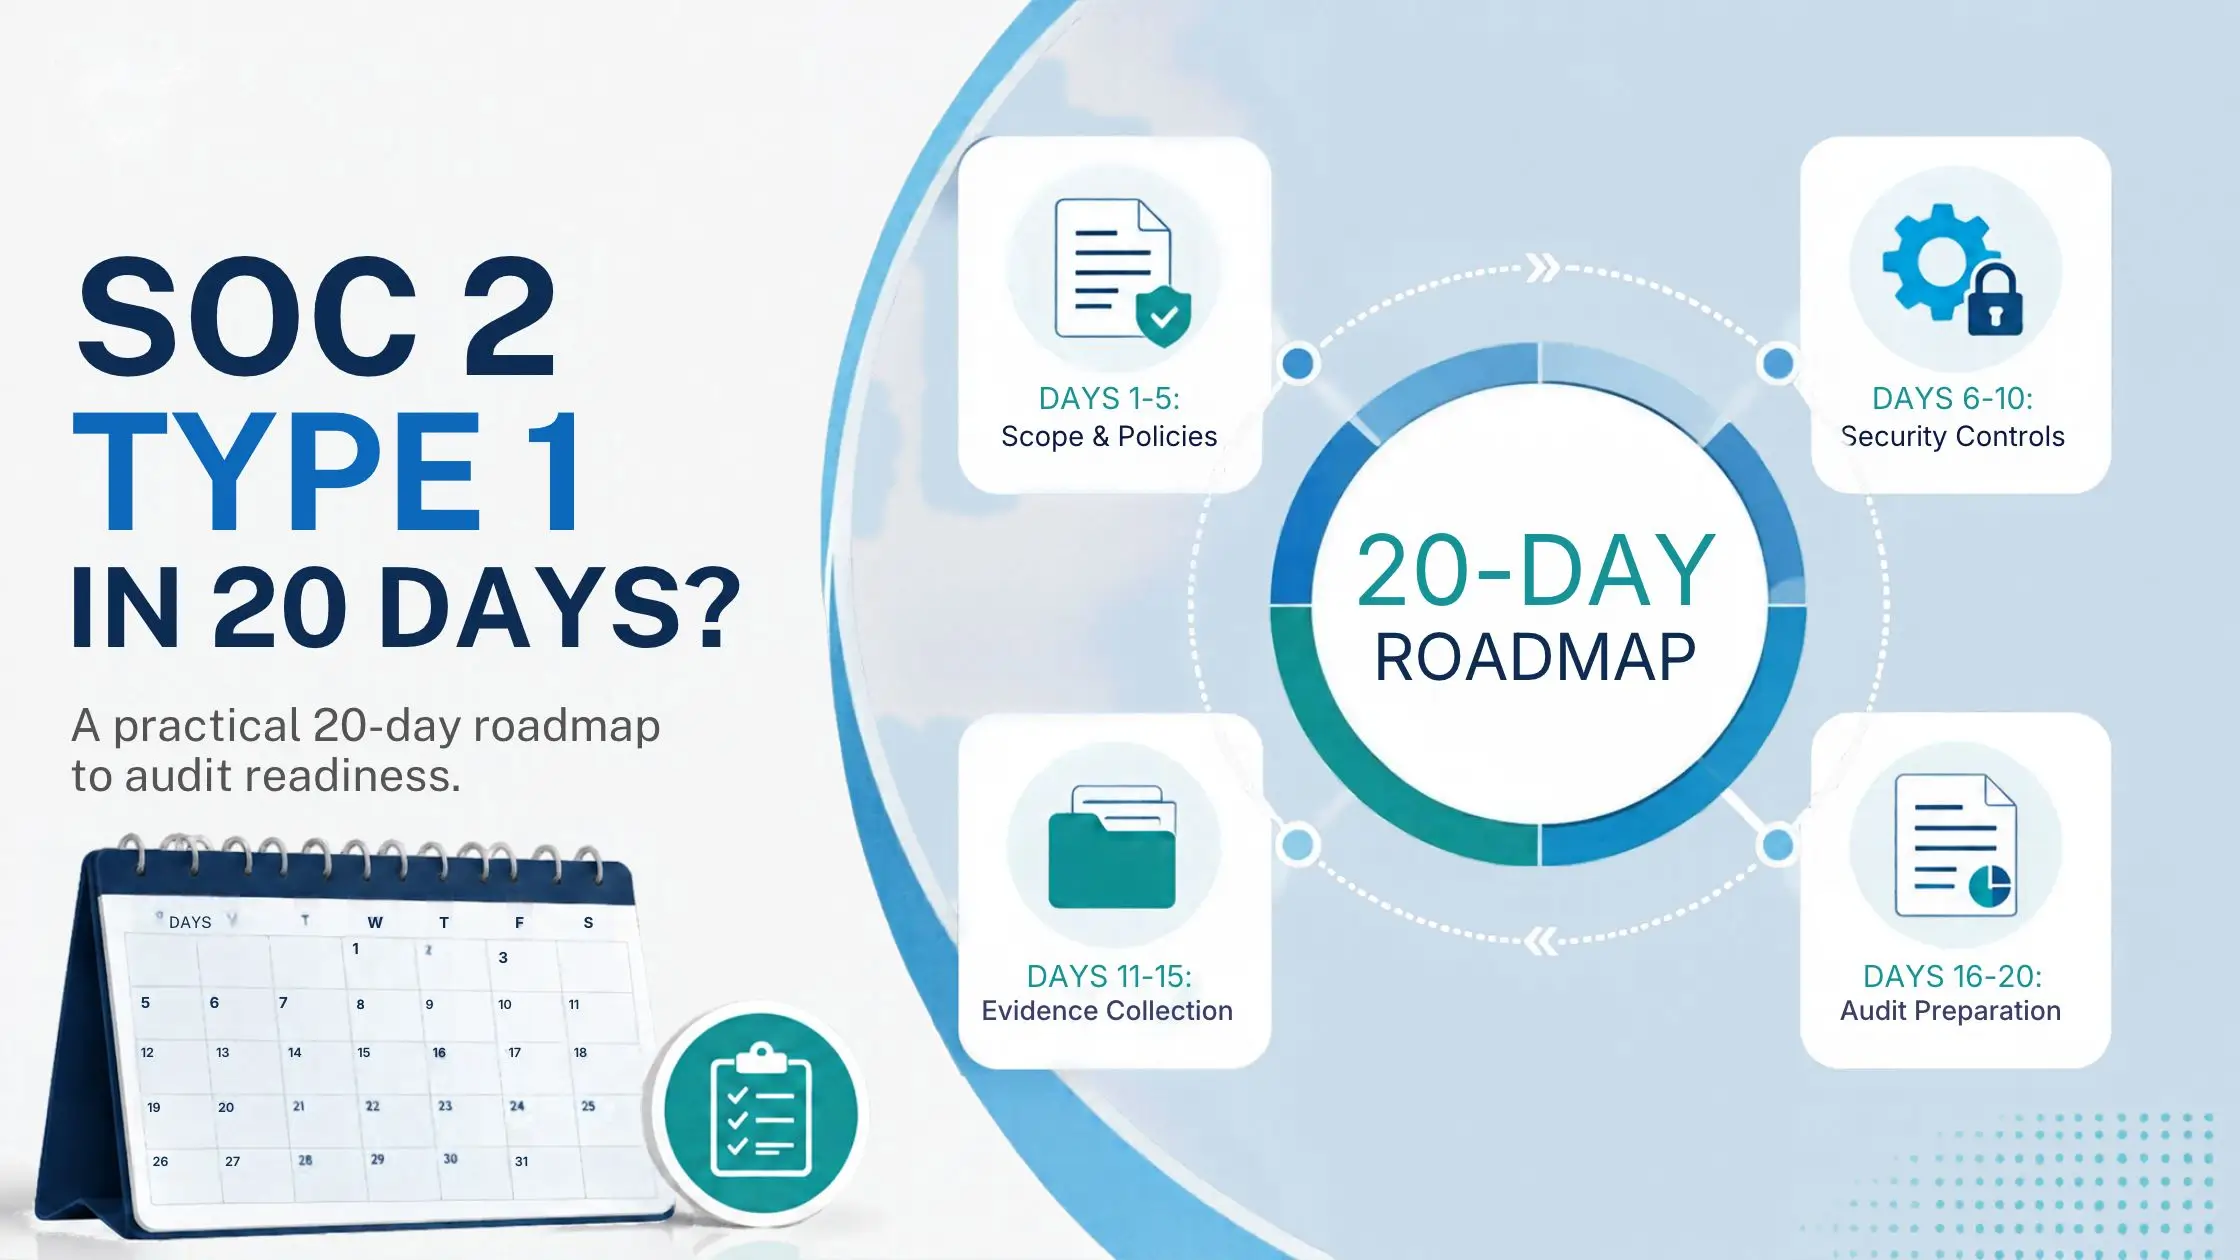
This plan breaks the preparation work into four manageable weekly phases:
The first step is to decide what is in the audit and identify what is missing.
Day 1: Map your infrastructure. List all servers, cloud accounts, databases, code repositories, and SaaS tools that touch customer data.
Day 2: Choose your criteria. Security is required; decide if your customers also require Availability or Confidentiality.
Day 3: Review current practices. Compare your daily workflows against the standard criteria.
Day 4: Build a gap list. Note any gaps that you've identified, for instance accounts that don't have 2FA or deployment steps that aren't documented.
Day 5: Assign responsibilities. Pick owners across your technical team for each task on the fix list.
Auditors need to read your rules before they check if you follow them. These policies should reflect how your team actually works.
Day 6: Information security basics. Write clear rules for device usage, workstation locking, and sensitive data handling.
Day 7: Access management rules. Document how team members gain access to tools, how privileges are reviewed, and how quickly access is revoked when someone leaves.
Day 8: Change management workflow. Document how code moves from development to production, including peer code reviews and automated tests.
Day 9: Incident response and backups. Outline who to contact in the event of an outage or breach, and detail how data is restored.
Day 10: Vendor checks and staff training. Review key third-party vendors and ensure all team members complete basic security awareness training.
During this week, your team applies the technical safeguards defined in your policies.
Day 11: Tighten access controls. Turn on multi-factor authentication (MFA) across all cloud dashboards and enforce single sign-on (SSO).
Day 12: Verify encryption. Make sure data is encrypted both in transit (using modern TLS) and at rest across your databases and storage buckets.
Day 13: Centralize activity logs. Enable audit logging across your cloud environments to see who accessed what and when.
Day 14: Run security scans. Scan your code and cloud infrastructure for vulnerabilities, and fix any urgent issues that surface.
Day 15: Test data recovery. Run a test restore from a recent database backup and document the results.
The final week is all about collecting the proof your auditor will request.
Day 16: Write the system description. Outline your software architecture, data flow diagrams, and company background.
Day 17: Gather screenshots and logs. Save evidence, such as configuration screens, sample code reviews, and policy acknowledgments, in organized folders.
Day 18: Run an internal mock review. Walk through your evidence with an advisor to spot any missing files or confusing answers.
Day 19: Clear up loose ends. Address any small gaps or missing screenshots identified during the practice review.
Day 20: Prepare the auditor package. Hand over your organized evidence and system documentation to your independent CPA firm.
Preparing for compliance while running day-to-day engineering operations can stretch internal bandwidth. Aanetic delivers comprehensive readiness and compliance consulting designed to streamline governance tasks, eliminate ambiguity, and build sustainable security controls.
Aanetic helps organizations define very clear audit boundaries so you don't end up with an overly complicated assessment by including internal tools outside the audit scope or data environments that aren't relevant.
Instead of generic policy libraries that create impossible operational burdens, Aanetic supplies modular, auditor-aligned policy frameworks tailored to your actual cloud architecture and workflow realities.
Aanetic partners with your engineering and DevOps teams to turn complex AICPA Trust Services Criteria into clear cloud settings, access control steps, and monitoring standards.
By conducting thorough readiness assessments and having the evidence in place before the formal audit engagement, Aanetic helps reduce friction in CPA reviews and minimize admin rework.
Navigating compliance without a clear plan can tire out your engineers, slow down sales, and leave your documentation messy. A structured 20-day roadmap, with help from Aanetic’s advisory team, turns a confusing checklist into an organized, step-by-step project.
Here are the key operational and strategic benefits of preparing for SOC 2 Type 1 with Aanetic:
Saves Critical Engineering Bandwidth: Instead of having your developers spend dozens of hours interpreting legal and technical AICPA guidelines, Aanetic translates complex requirements into clear, everyday tasks. Your engineers focus only on specific configurations while continuing to ship product features.
Keeps Your Audit Boundary Tight: Fast-growing companies often overscope by auditing systems that don’t handle sensitive customer data. Aanetic does targeted scoping early to set clear audit boundaries, saving time and avoiding extra admin work.
Replaces Generic Templates with Usable Policies: Many teams download rigid policy templates that disrupt normal workflows. Aanetic provides modular, cloud-aligned governance frameworks that match how modern software teams actually operate, making them easy to implement and maintain.
Reduces Friction During CPA Review: Independent auditors look for specific, well-organized evidence. Aanetic helps structure your evidence folders, runs internal readiness checks, and verifies system descriptions before audit day, so your formal CPA review moves forward with minimal back-and-forth.
Builds a Smooth Path Toward Type 2: Working with Aanetic is more than a one-time task. It establishes clear routines for change management, access controls, and logging, providing the foundation you need as you move to a longer SOC 2 Type 2 review.
Showing strong security controls builds customer trust and clears sales roadblocks. Using a focused 20-day SOC 2 Type 1 readiness plan gives your team an efficient way to get audit-ready without getting lost in complexity.
With Aanetic’s structured support, you can turn compliance needs into simple, lasting security habits. Contact the Aanetic team to talk about your scope and start your 20-day plan.
A SOC 2 Type 1 assessment assesses whether your security controls are set up correctly at a specific point in time. A Type 2 audit checks if those controls actually work well over a longer period, usually between 3 and 12 months.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
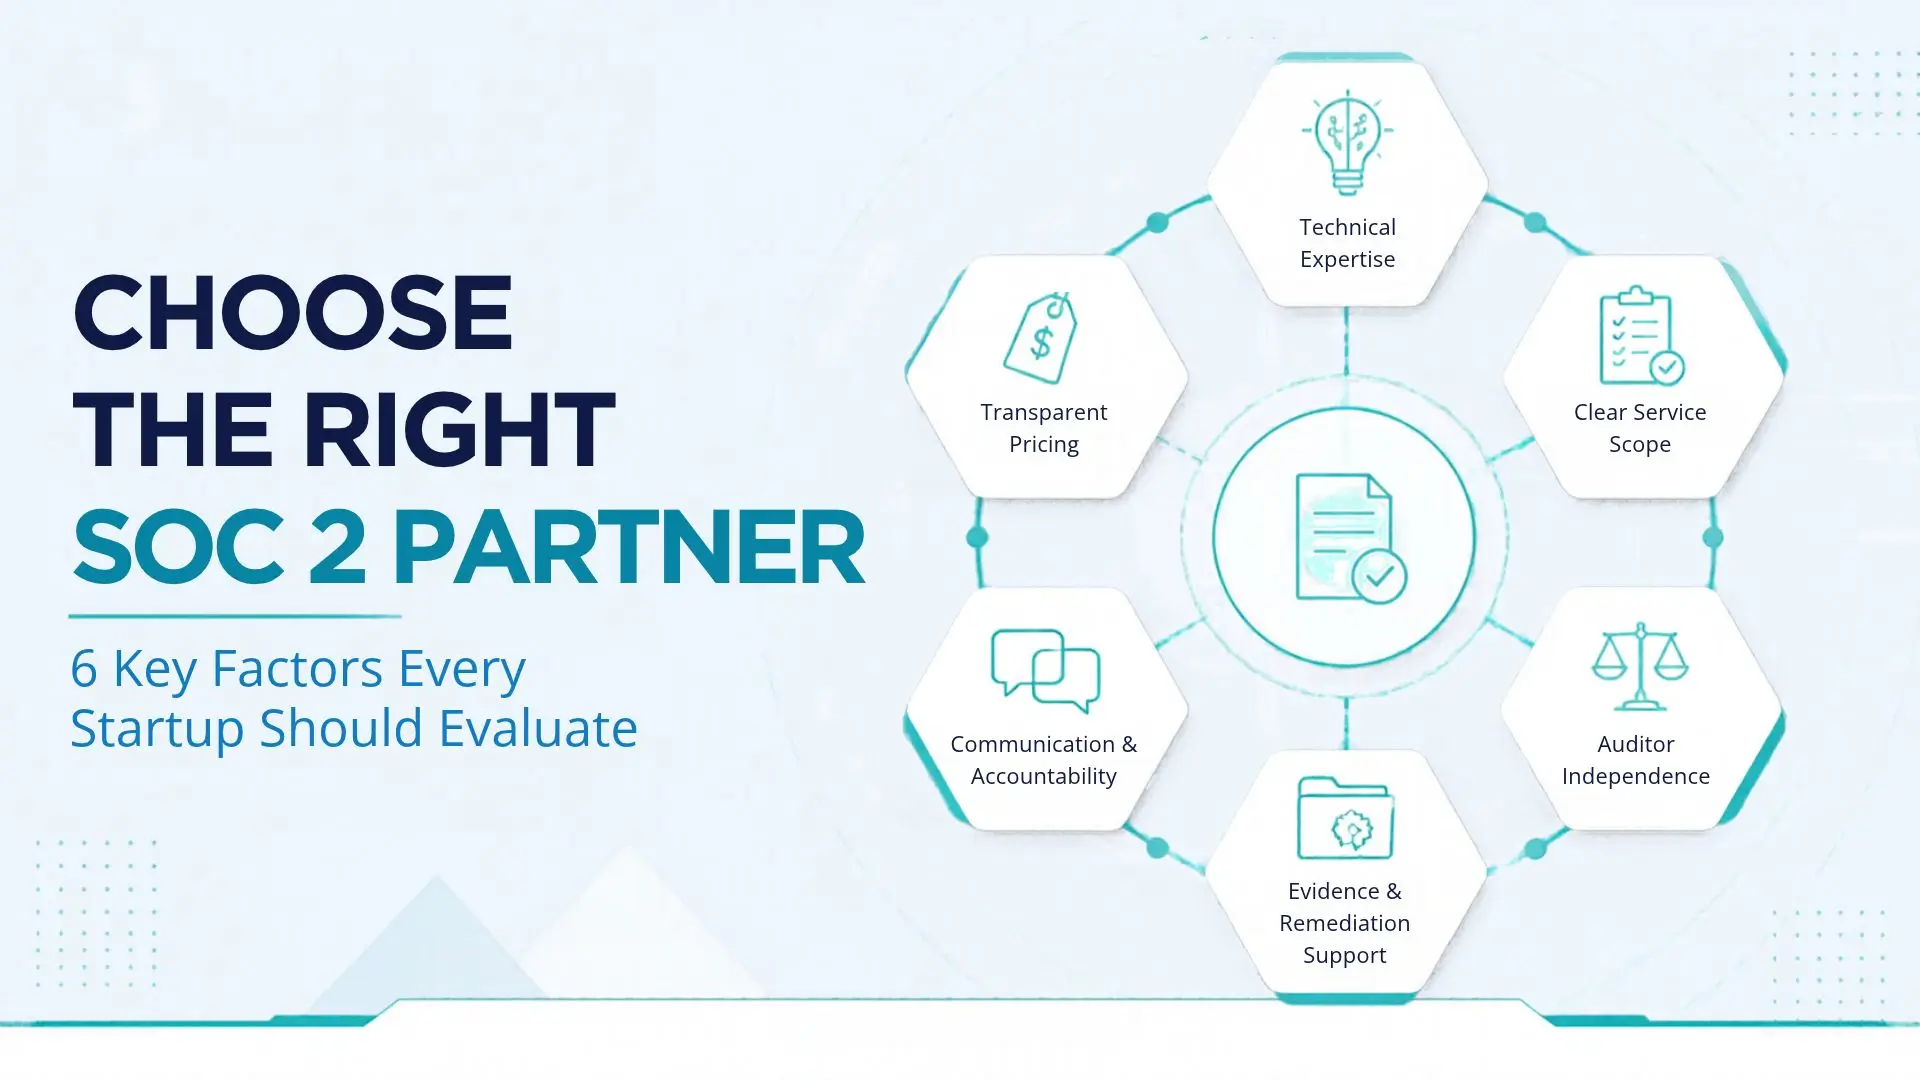
Get fast, budget-friendly SOC 2 compliance for your startup. Streamline gap analysis, automate evidence collection, and pass your audit with Aanetic.
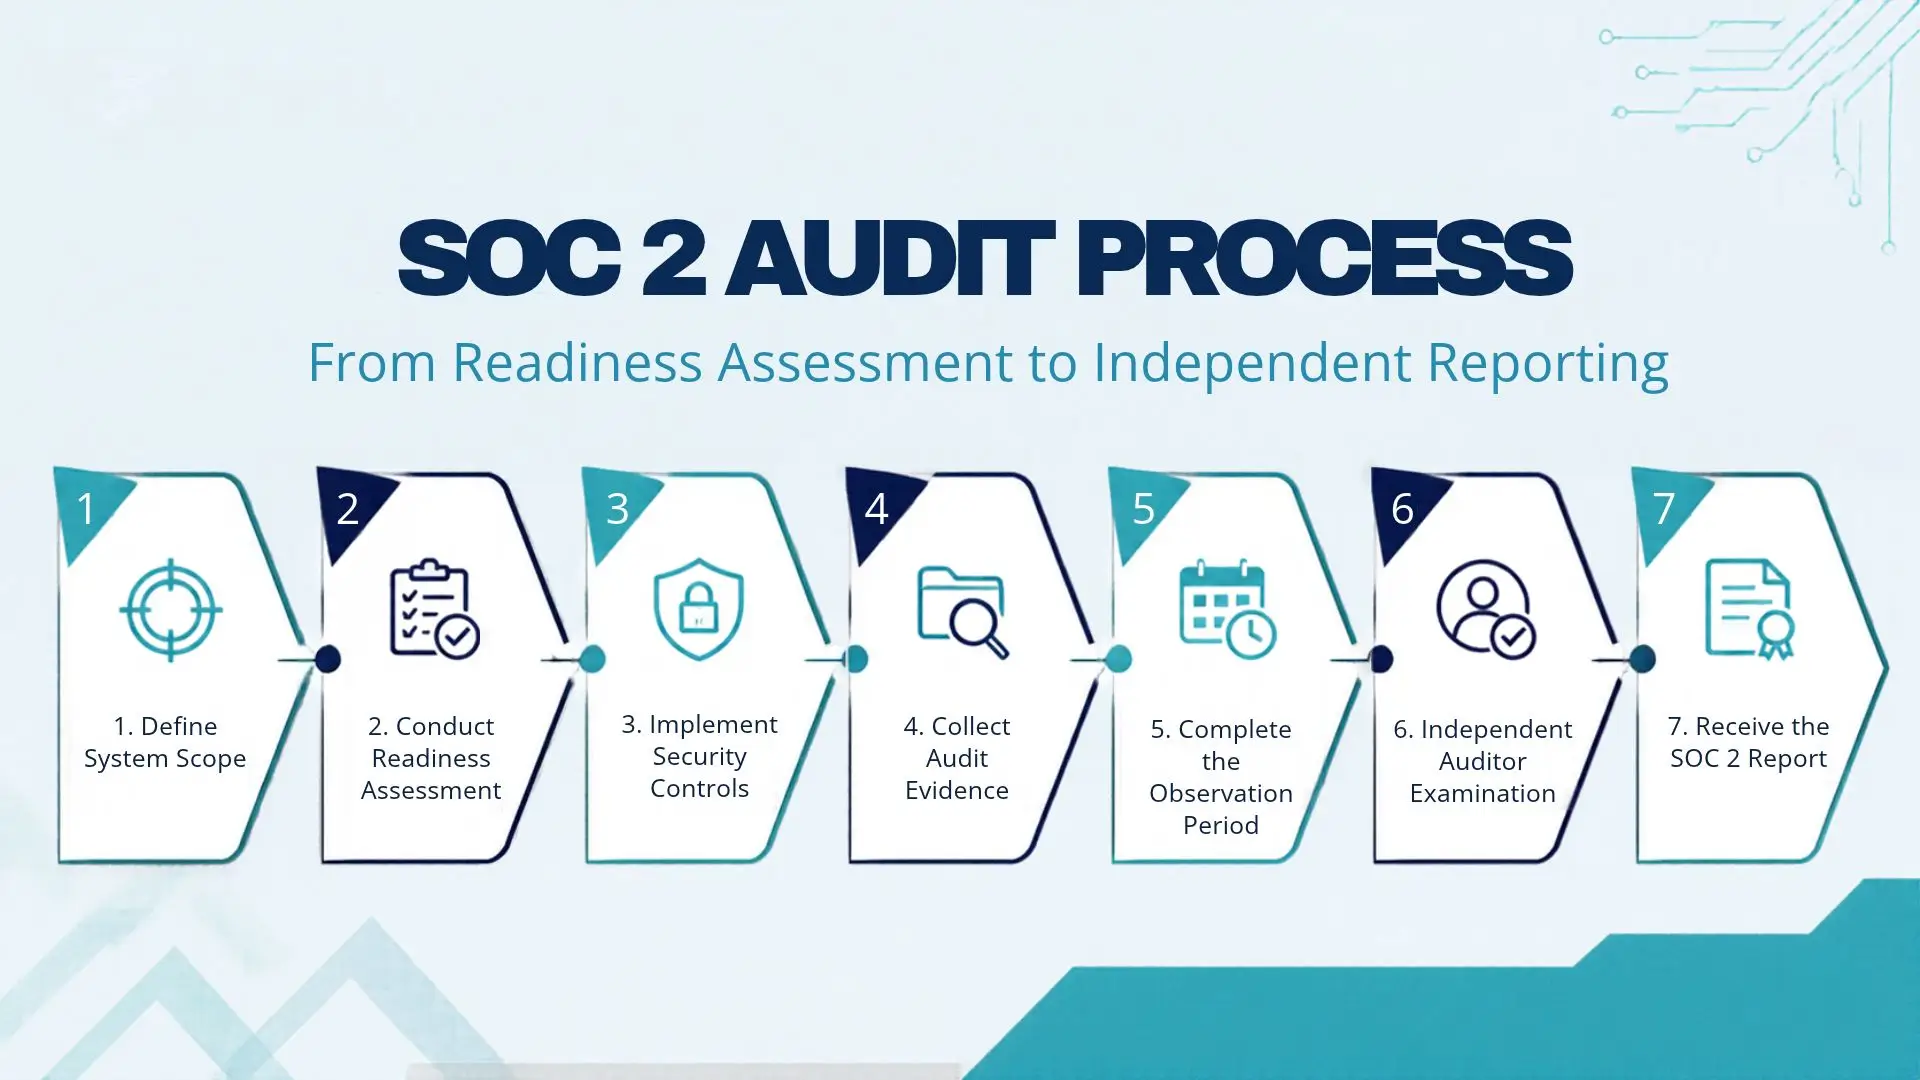
Explore the top SOC 2 audit challenges for Indian startups, from scoping errors to access gaps, and see how Aanetic simplifies the pathway to attestation.
Fast-track SOC 1 and SOC 2 readiness for 2027 with Aanetic. Identify compliance gaps, improve controls, organize evidence, and prepare for an independent audit.