28 October 2026
|6:14 pm
|Aanetic Advisory Editorial
Get fast, budget-friendly SOC 2 compliance for your startup. Streamline gap analysis, automate evidence collection, and pass your audit with Aanetic.
Winning mid-market and enterprise deals requires proof that customer data remains secure. For high-growth SaaS and tech startups, achieving a System and Organization Controls (SOC) 2 report can help clear enterprise procurement barriers, address third-party risk assessments, and support critical sales opportunities.
SOC 2 is an independent attestation rather than a simple software switch. Getting to SOC 2 requires proper scoping, formalization of your policies, ongoing control monitoring, and the collection of audit evidence. The right partner can make that journey much easier and reduce the amount of engineering effort you end up with.
Here is what founders, CTOs, and compliance leaders must evaluate when choosing a reliable SOC 2 partner, along with how Aanetic simplifies the journey from readiness to independent examination.
Many founders assume compliance involves buying an automated dashboard or downloading policy templates. In practice, copy-pasting policies rarely holds up under CPA scrutiny.
Startups face unique constraints:
Engineering Bandwidth: Developers should focus on building features, not spending days taking screenshots or writing security manuals.
Dynamic Tech Stacks: Cloud-native microservices, modern CI/CD pipelines, and multi-tenant setups need custom controls instead of old, rigid checklists.
Audit Fatigue: If your Trust Services Criteria (TSC) aren’t set right, you can end up with too much in scope, which makes audits take longer and cost more.
A credible partner serves as an end-to-end guide through scoping, remediation, and final attestation.
Before making your final decision, avoid these common mistakes:
Choosing Only Based on Price: A low initial quote may exclude important services or additional costs.
Believing Guaranteed Results: No readiness provider should guarantee an unqualified SOC 2 opinion before an independent examination.
Ignoring Auditor Independence: Always understand who performs the examination and whether professional independence requirements are satisfied.
Overlooking Technical Expertise: Your provider should understand your infrastructure, applications, and security requirements.
Ignoring Internal Responsibilities: SOC 2 requires active participation from your own team. External support cannot replace operating your controls.
Focusing Only on Certification: Your security practices should remain effective beyond the initial reporting process.
Not all compliance partners operate the same way. Some merely offer software dashboards that spit out templates, leaving your engineering leads to figure out the actual cloud remediation. Others act purely as traditional auditing firms without modern tooling.
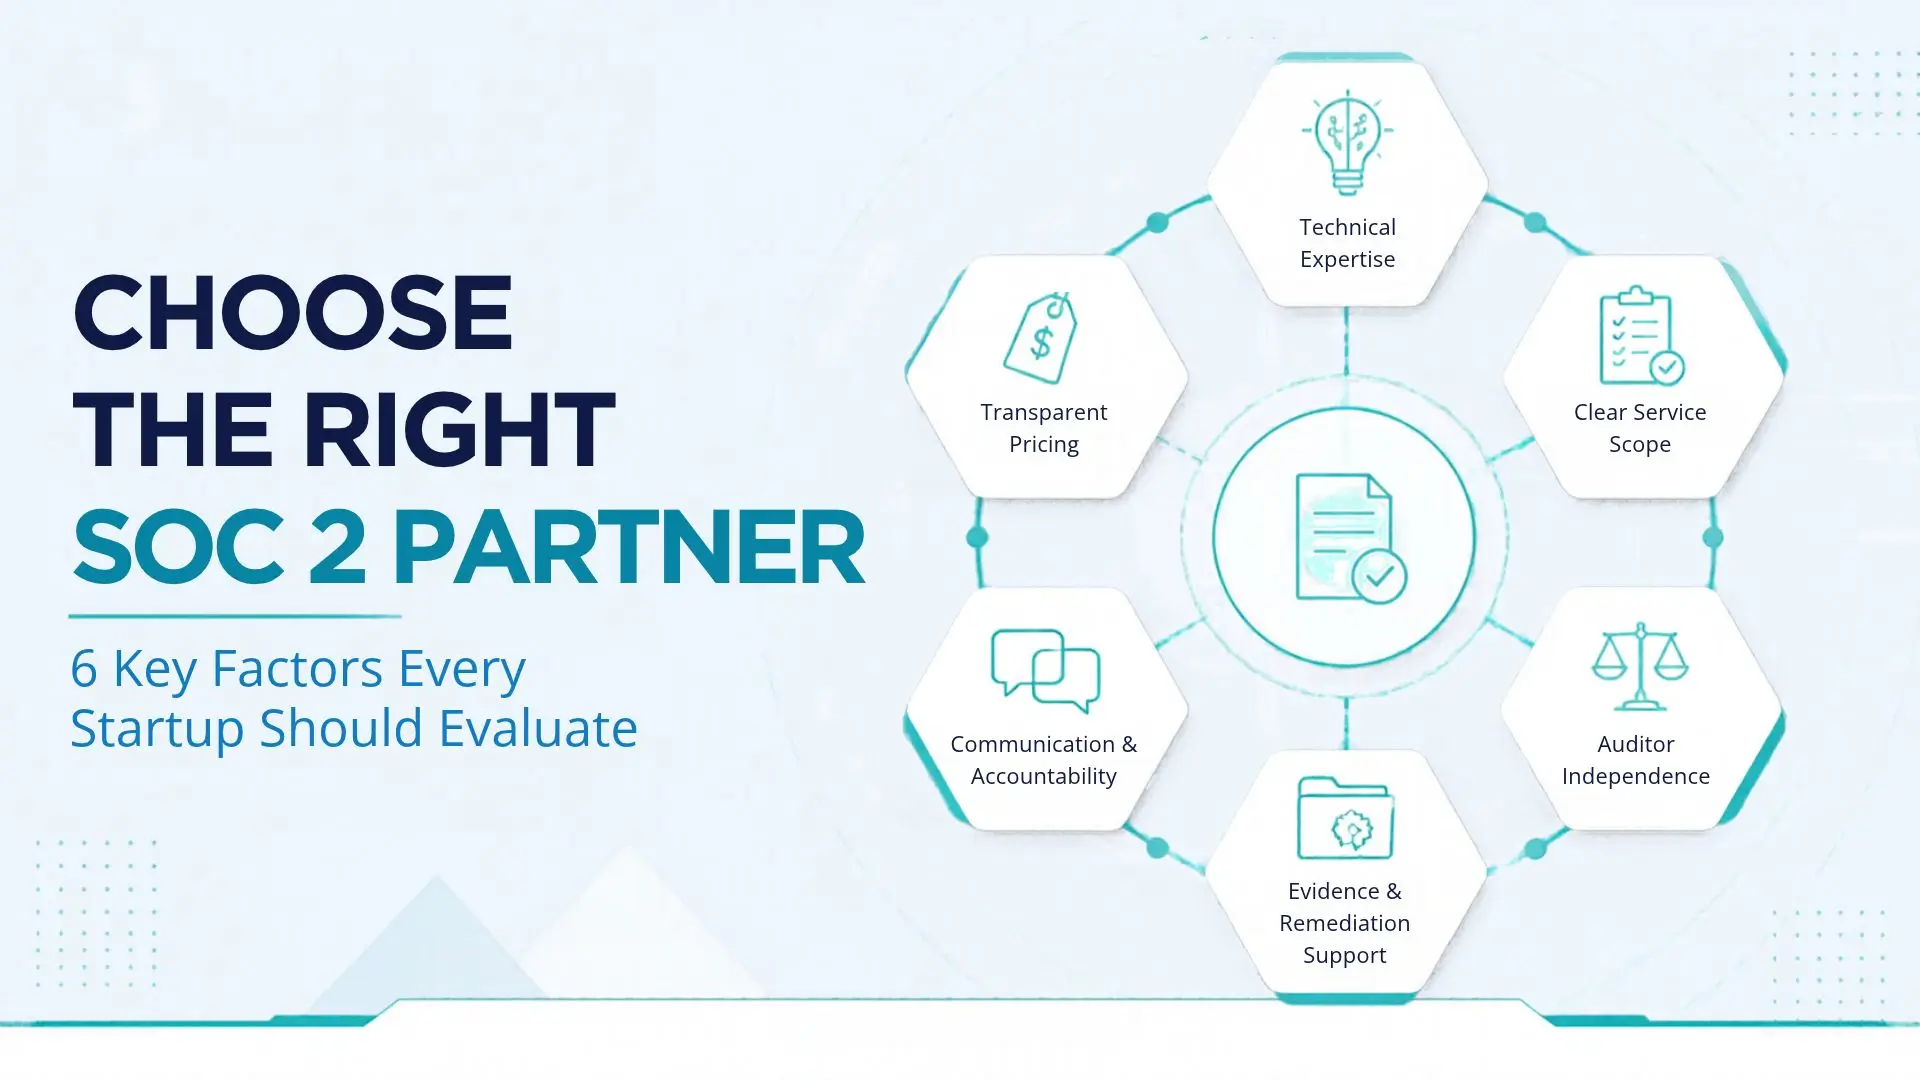
When evaluating potential providers, look for these foundational attributes:
Your provider must understand modern cloud infrastructure—AWS, GCP, Azure, Kubernetes, and API-driven services. Traditional IT audit methodologies often struggle with containerized environments, serverless workflows, and modern identity providers (IdPs), leading to friction and irrelevant audit requests.
The Security criterion is required, but Availability, Confidentiality, Processing Integrity, and Privacy are optional. A good advisor helps you find your Minimum Viable Scope, so you protect production data without including extra internal systems in the audit.
It’s normal to find control gaps during a readiness check. What matters is whether your provider gives you a list of problems or actually helps you fix them, like setting up MFA, RBAC, log retention, and vendor risk levels.
Only an independent, licensed CPA firm can issue SOC 2 reports. A reliable provider works closely with accredited auditors and helps turn your technical setup into audit-ready materials, so you don’t face surprises during the review.
Type 1: Evaluates whether controls are properly designed at a specific point in time (ideal for unblocking immediate sales deals).
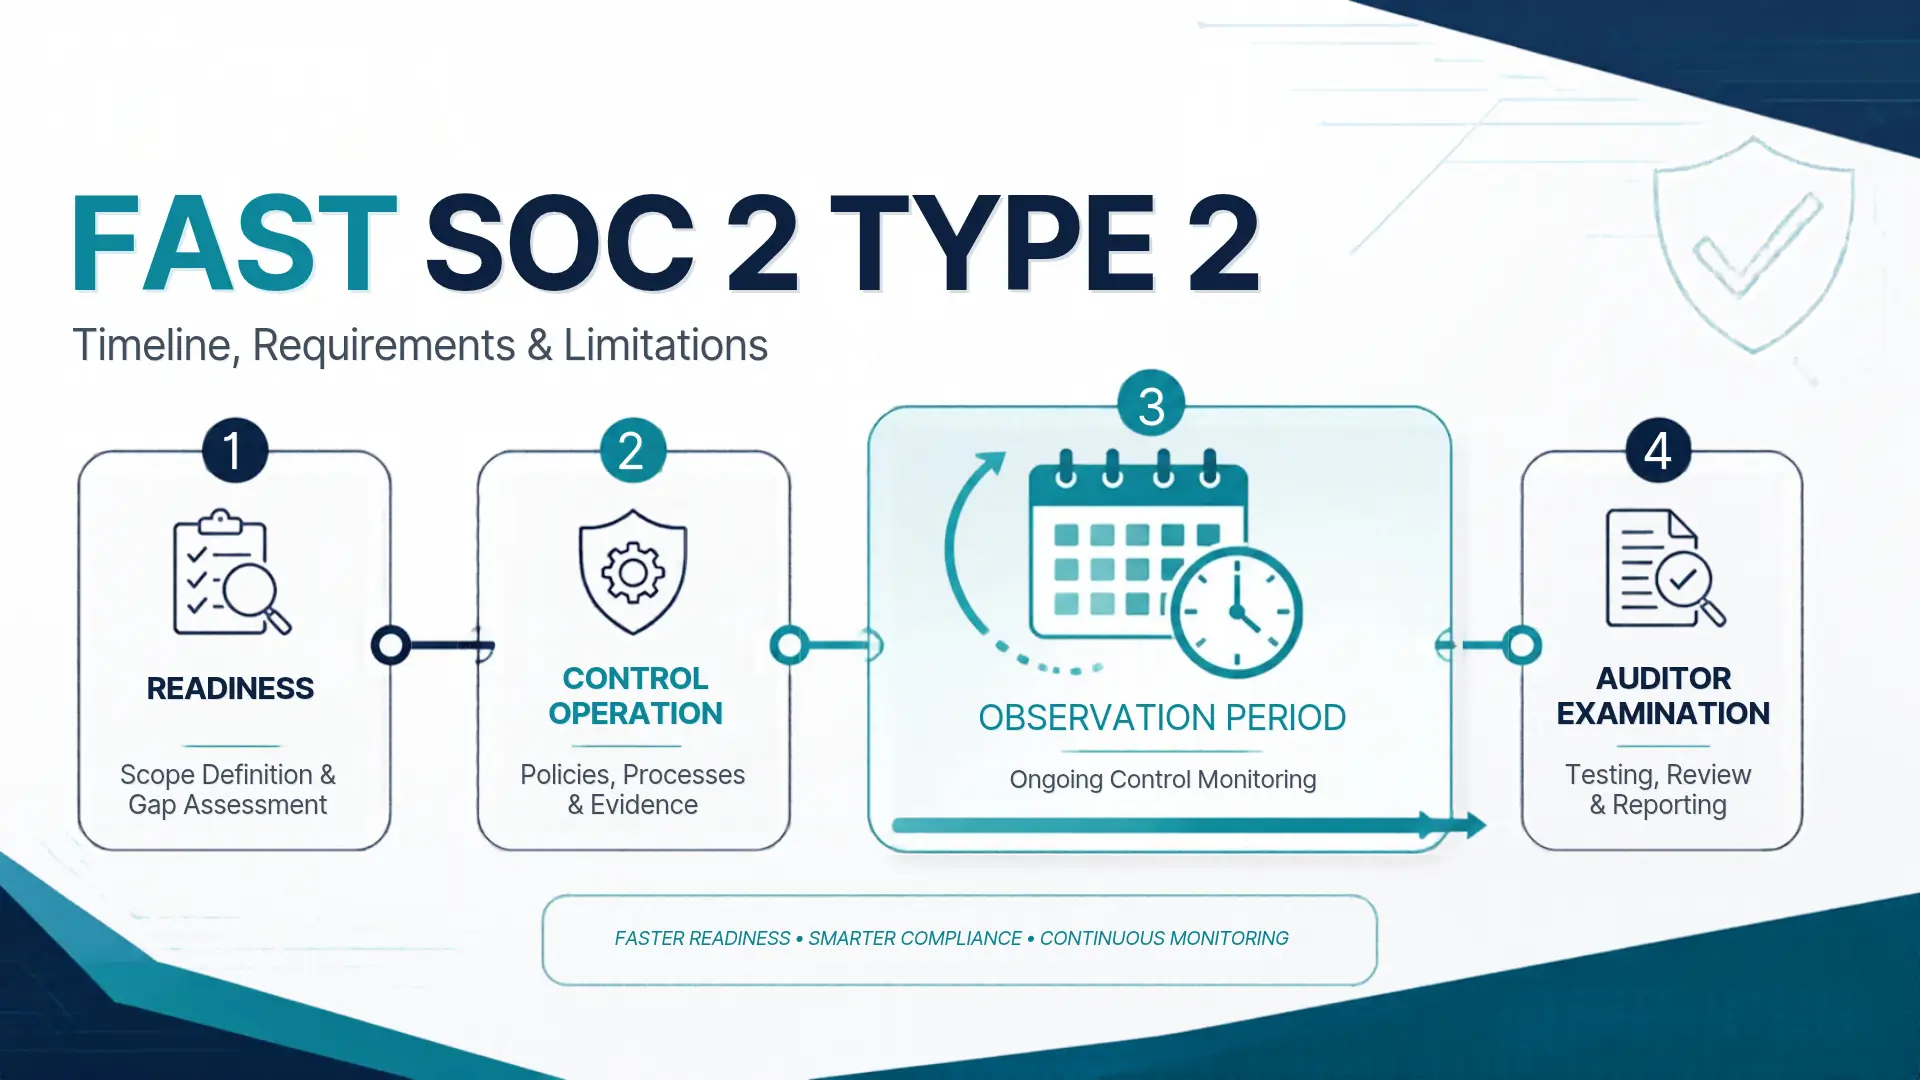
Type 2: Checks if your controls worked well over a period of 3 to 12 months. Your provider should show you a clear path from Type 1 to ongoing Type 2 compliance.
Traditional IT consultancies treat compliance like a bureaucratic paperwork exercise with 50-page binders. Automated tools, on the other hand, often leave teams with an alert-heavy dashboard and zero execution support.
Aanetic operates at the intersection of hands-on security engineering and advisory. We don’t just flag what’s broken; we work alongside your engineering and DevOps teams to fix it.
Zero Engineering Drag: Aanetic handles policy authoring, evidence structuring, and control design so your core team stays focused on product shipping.
Cloud-Native & AI-Aware Readiness: Today’s SaaS companies use serverless setups, microservices, and AI. Aanetic knows how to secure containers, manage LLM data, and handle modern IAM, so your controls fit your real infrastructure.
Integrated VAPT & Risk Assessments: SOC 2 demands rigorous testing. Aanetic bundles hands-on Vulnerability Assessment and Penetration Testing (VAPT) into a single unified engagement to meet critical auditor requirements.
Direct Auditor Defense: Aanetic bridges the technical gap between your development stack and CPA-accredited auditors, eliminating miscommunications and avoiding endless audit revisions.
Aanetic follows an agile, transparent framework designed to get startups certified without operational friction:
Precision Scoping: We identify your exact Trust Services Criteria (TSC), so you never waste engineering bandwidth on non-production systems or out-of-scope tools.
Hands-On Remediation: Rather than generic recommendations, Aanetic provides turnkey security policies, infrastructure hardening guidelines, and streamlined evidence pipelines.
Technical Validation: Before the auditor steps in, Aanetic conducts an internal dry-run audit alongside penetration testing to ensure there are no surprise non-conformities.
Auditor Defense & Sign-off: Aanetic stays in the room during evidence walkthroughs with licensed CPA partners to defend control design and answer auditor queries directly.
At Aanetic, we understand that fast-moving startups cannot afford to pause product roadmaps for bureaucratic compliance exercises. Aanetic approaches governance, risk, and compliance (GRC) through an engineering-first, pragmatic lens.
Aanetic’s compliance experts evaluate your cloud architecture, products, and operational workflows to design a scoped compliance blueprint. We eliminate redundant controls and focus strictly on what satisfies auditors and unlocks your target enterprise deals.
Aanetic integrates with your existing developer stack and cloud environments to automate evidence collection. Continuous monitoring ensures you avoid compliance drift and remain audit-ready all year, rather than scrambling a week before your annual review.
Beyond technology, Aanetic acts as an extension of your internal team. Our compliance specialists assist in drafting tailored infosec policies, conducting thorough internal risk assessments, running mock audits, and coordinating with independent CPA auditors to ensure an unqualified audit report.
If you plan to expand internationally or enter regulated industries, Aanetic can map your SOC 2 controls to frameworks like ISO 27001, HIPAA, and GDPR. This lets you scale without starting over.
Enterprise customers want more than a security badge. They need to trust that your real security practices protect their data.
With Aanetic, you don’t get cookie-cutter policies or generic dashboards. You get a dedicated security partner that designs pragmatic controls, fast-tracks your readiness assessment, and ensures your SOC 2 attestation is sealed smoothly.
Start your SOC 2 journey now. Schedule a Free Scoping Call with Aanetic's GRC Specialists
A readiness partner helps you get your infrastructure, policies, and evidence workflows in order. Only an independent, licensed CPA firm can do the examination and issue the final SOC 2 attestation report.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
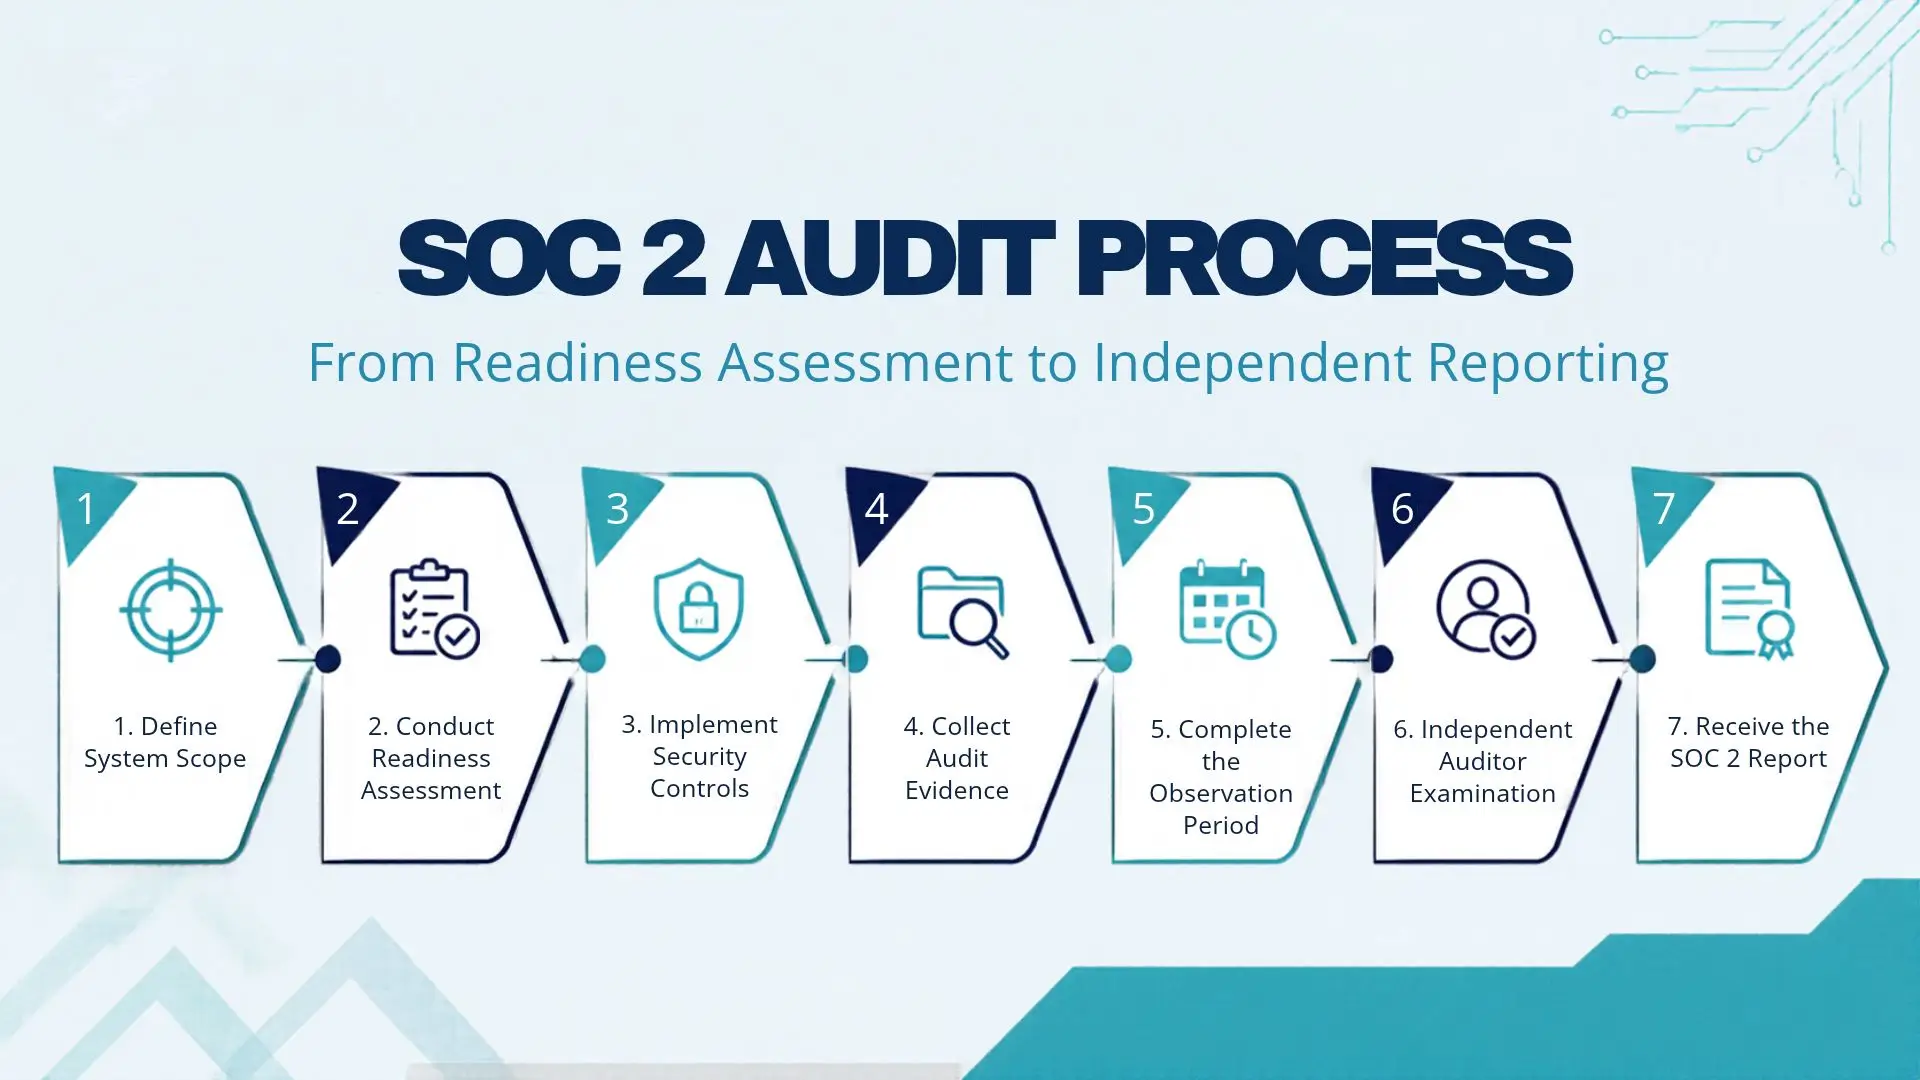
Explore the top SOC 2 audit challenges for Indian startups, from scoping errors to access gaps, and see how Aanetic simplifies the pathway to attestation.
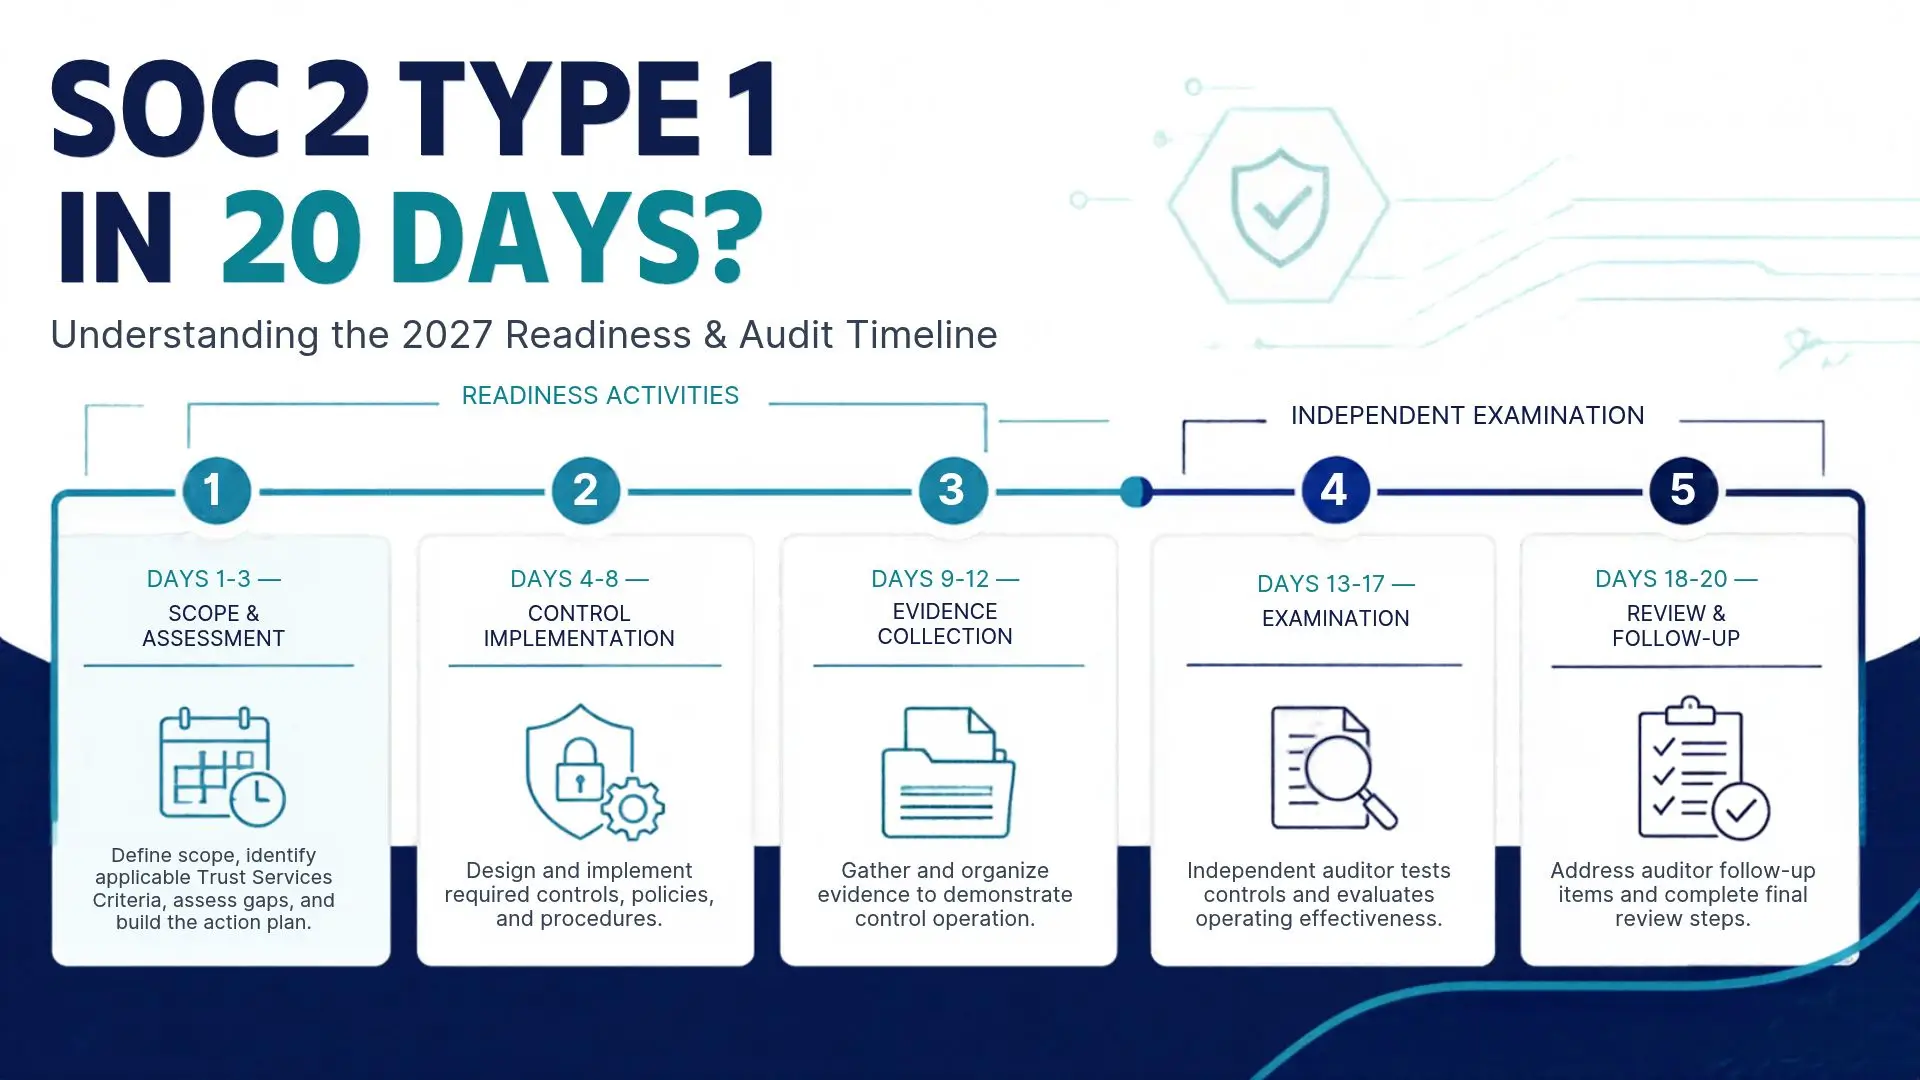
Fast-track SOC 1 and SOC 2 readiness for 2027 with Aanetic. Identify compliance gaps, improve controls, organize evidence, and prepare for an independent audit.
Learn how to fast-track SOC 2 Type 2 with efficient readiness planning, compliance automation, evidence collection, and Aanetic's technology-enabled approach.