4 November 2026
|3:40 pm
|Aanetic Advisory Editorial
Learn how to accelerate SOC 2 audit readiness with automation, evidence collection, control mapping, and expert compliance support from Aanetic.
Enterprise procurement can get delayed during security reviews. When key prospects request a SOC 2 report to verify data protection, engineering teams face a choice: pause product work to gather compliance evidence or risk revenue delays.
In the past, doing this manually took 3 to 6 months of internal effort. You had to take configuration screenshots, write numerous policy documents, and coordinate repeatedly with stakeholders across the business.
Modern compliance engineering changes this process. By moving from manual checks to automated evidence collection and ongoing controls mapping, fast-growing tech companies can become SOC 2 audit-ready in days rather than months, without interrupting their main engineering work.
For most organizations, the delays in SOC 2 readiness stem from workflow bottlenecks rather than weak technical security:
Fragmented Cloud Infrastructure: Engineering teams use multiple platforms, including AWS, Google Cloud, GitHub, GitLab, Okta, and Jira. Manually checking configurations in each tool takes days of developer time.
Manual Evidence Gathering: Gathering point-in-time screenshots, access review logs, code review tickets, and employee training completions creates significant administrative overhead.
Policy Paralysis: Creating 20 to 30 custom governance policies (covering Incident Response, Change Management, Access Control, and Business Continuity) from scratch often leads to weeks of drafting and revision.
Unclear Audit Scoping: Including irrelevant services or environments inflates the audit scope, demanding unnecessary documentation and control verification.
To achieve fast compliance, it is important to clearly separate the preparation phase from the formal external evaluation process:
Audit readiness is the internal baseline phase. This means defining the scope, setting up technical security controls, creating organizational policies, and collecting verifiable evidence mapped to the AICPA Trust Services Criteria. With automated discovery and continuous controls mapping, you can achieve audit readiness in days rather than months.
A SOC 2 Type 1 report examines whether control designs meet criteria at a single point in time. Once audit readiness is established, an independent licensed CPA firm can review pre-mapped evidence and deliver a Type 1 report to satisfy immediate procurement reviews.
A SOC 2 Type 2 report evaluates whether controls operated effectively over a designated testing period (typically 3 to 6 months). Achieving day-one readiness allows automated monitoring to capture continuous operational evidence throughout this window, removing the traditional scramble when the observation period concludes.
To speed up preparation, organizations focus on identifying the right controls within the AICPA Trust Services Criteria:
Security (Common Criteria): The mandatory baseline covering access control, logical and physical boundary protection, configuration management, vulnerability scanning, and incident response workflows.
Availability: Evaluates system capacity management, disaster recovery, automated backups, and incident recovery times for cloud services.
Confidentiality: Focuses on granular access permissions, data classification protocols, data retention policies, and enforcement of encryption standards.
Processing Integrity: Applied when systems execute automated financial transactions or critical computational logic requiring operational accuracy and monitoring.
Privacy: Applied to organizations managing personal information, aligning data subject access controls, consent handling, and disposal routines.
By using a clear, step-by-step workflow, technology organizations can complete the audit readiness phase in five key steps:
Determine exact service organization boundaries, cloud production environments, and third-party dependencies.
Connect identity providers, code repositories, and cloud workloads to extract baseline infrastructure states via programmatic APIs.
Run automated control evaluations against the AICPA Common Criteria.
Find missing multi-factor authentication (MFA), unencrypted data buckets, or public resource access points so you can fix them directly.
Formulate a centralized, documented risk register outlining technical and operational safeguards.
Implement auditor-aligned security policies, including Acceptable Use, Incident Response, Access Control, and Data Classification policies.
Automate employee security awareness training onboarding and collect digital policy acknowledgments.
Inventory all third-party software and subservice providers and evaluate potential supply chain and data exposure risks.
Enforce least-privilege principles, formalize role-based access reviews, and institute documented change management approval tracks.
Consolidate verified system logs, configuration proofs, and administrative policies into a centralized repository.
Enable secure, read-only auditor access to eliminate manual email attachments and disconnected shared folders.
Balancing technical security needs with daily engineering work requires clear guidance. Aanetic makes this easier by offering expert advice and simple compliance readiness methods.
Targeted Audit Scoping: Aanetic helps identify the relevant Trust Services Criteria and isolate production systems, preventing over-scoping and unnecessary overhead.
Pre-Built Governance and Policy Assets: Access pre-structured administrative and technical policy frameworks designed to align directly with auditor expectations.
Automated Evidence and Control Mapping: Aanetic’s structured workflows align cloud configurations and security settings to AICPA criteria, minimizing manual evidence collection and administrative burden.
Comprehensive Pre-Audit Readiness Reviews: Aanetic conducts mock walkthroughs and gap checks to ensure controls function effectively and identify fixes before outside CPA auditors begin their review.
Multi-Framework Efficiency: SOC 2 controls often overlap with the requirements of ISO 27001, PCI DSS, and the DPDP Act. They map controls across these standards to avoid repeating work.
Preparing for a SOC 2 audit does not have to stall your engineering roadmap or slow business momentum. By leveraging structured gap remediation, pre-built governance frameworks, and automated control mapping, you can achieve complete audit readiness efficiently and build lasting trust with enterprise customers.
Connect with the compliance specialists at Aanetic to assess your environment, streamline evidence collection, and prepare for your upcoming audit with confidence.
SOC 2 audit readiness means a company has finished its internal preparation. This includes defining the environment, implementing necessary security policies, setting up technical controls, and gathering evidence before the external auditor begins work.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
Looking for low-budget SOC 2 certification? Aanetic helps startups achieve SOC 2 compliance with cost-effective solutions and expert guidance.
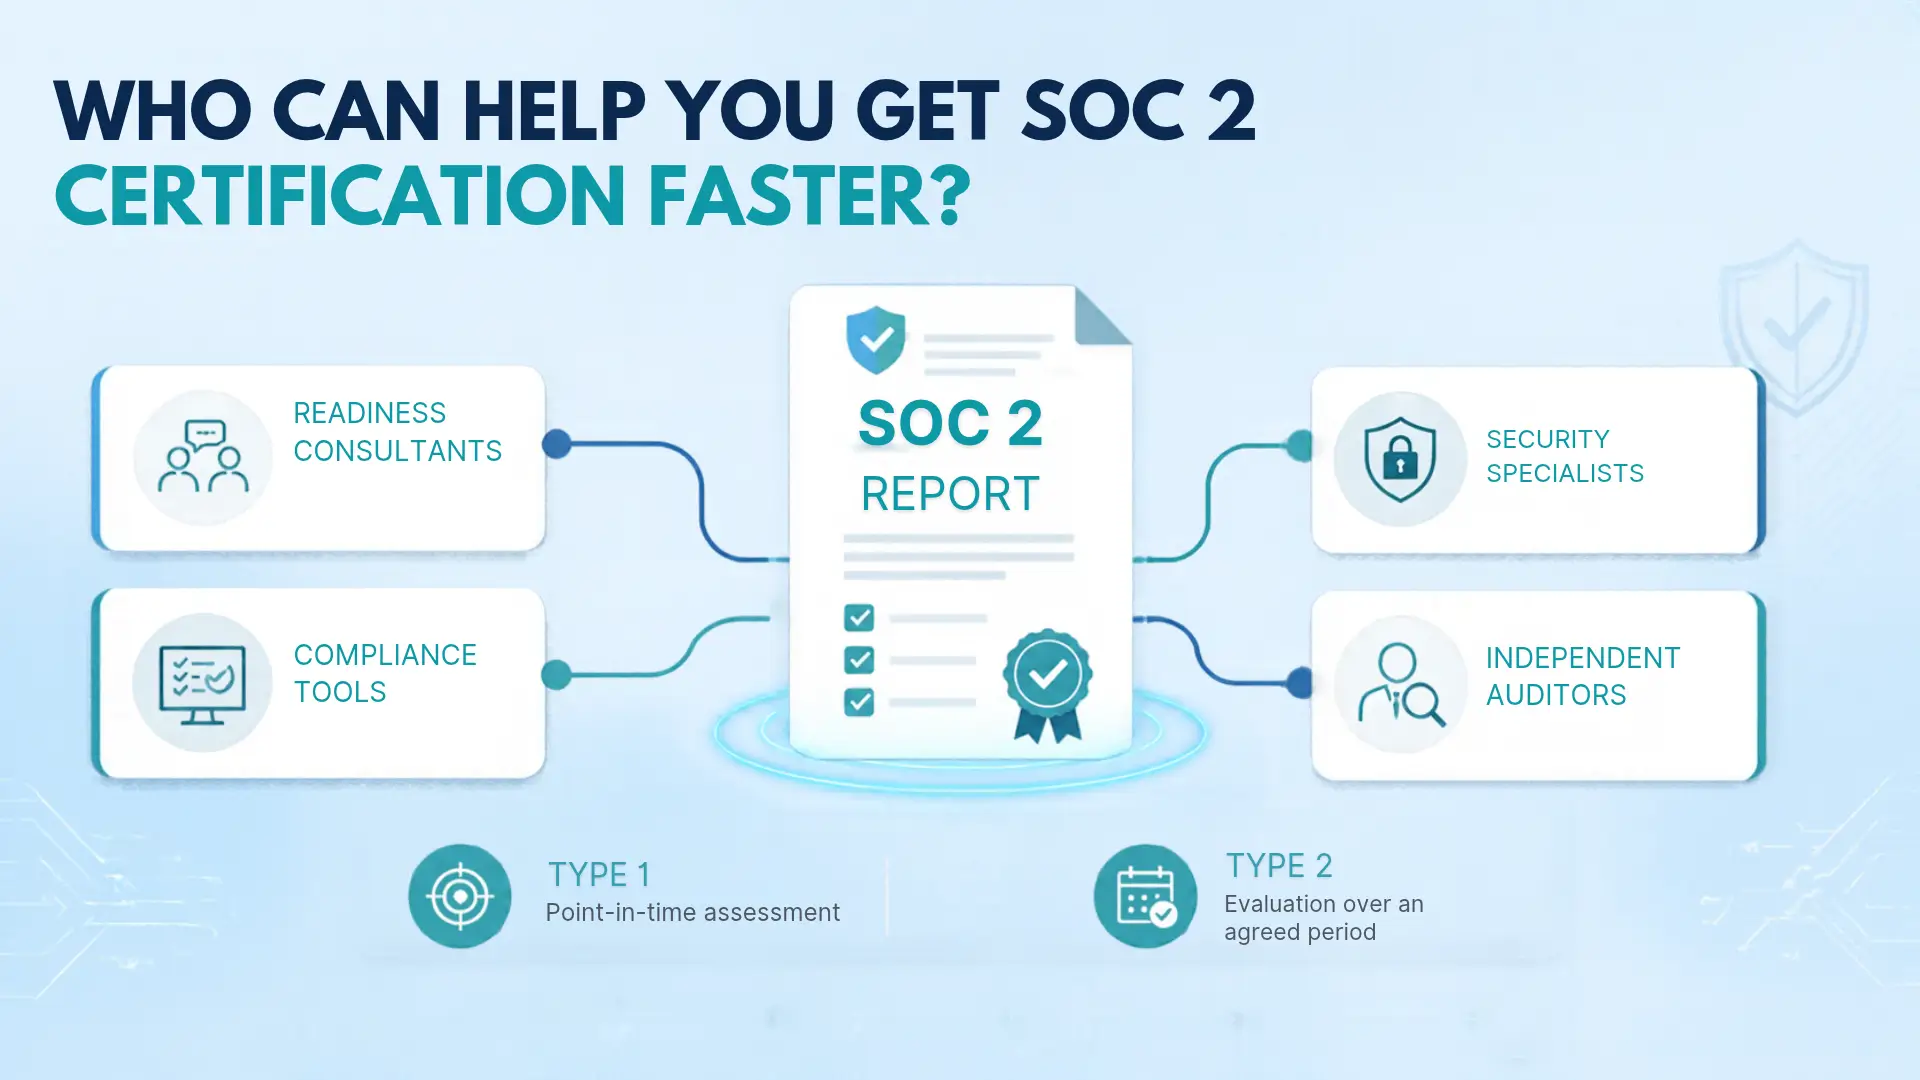
Looking for faster SOC 2 certification? Explore how the right compliance provider can simplify audits, reduce delays, and accelerate your SOC 2 journey.
Looking for the top SOC 2 certification provider in India in 2026? Learn how Aanetic streamlines SOC 2 Type 1 and Type 2 readiness and audit support for SaaS.