17 November 2026
|9:46 am
|Aanetic Advisory Editorial
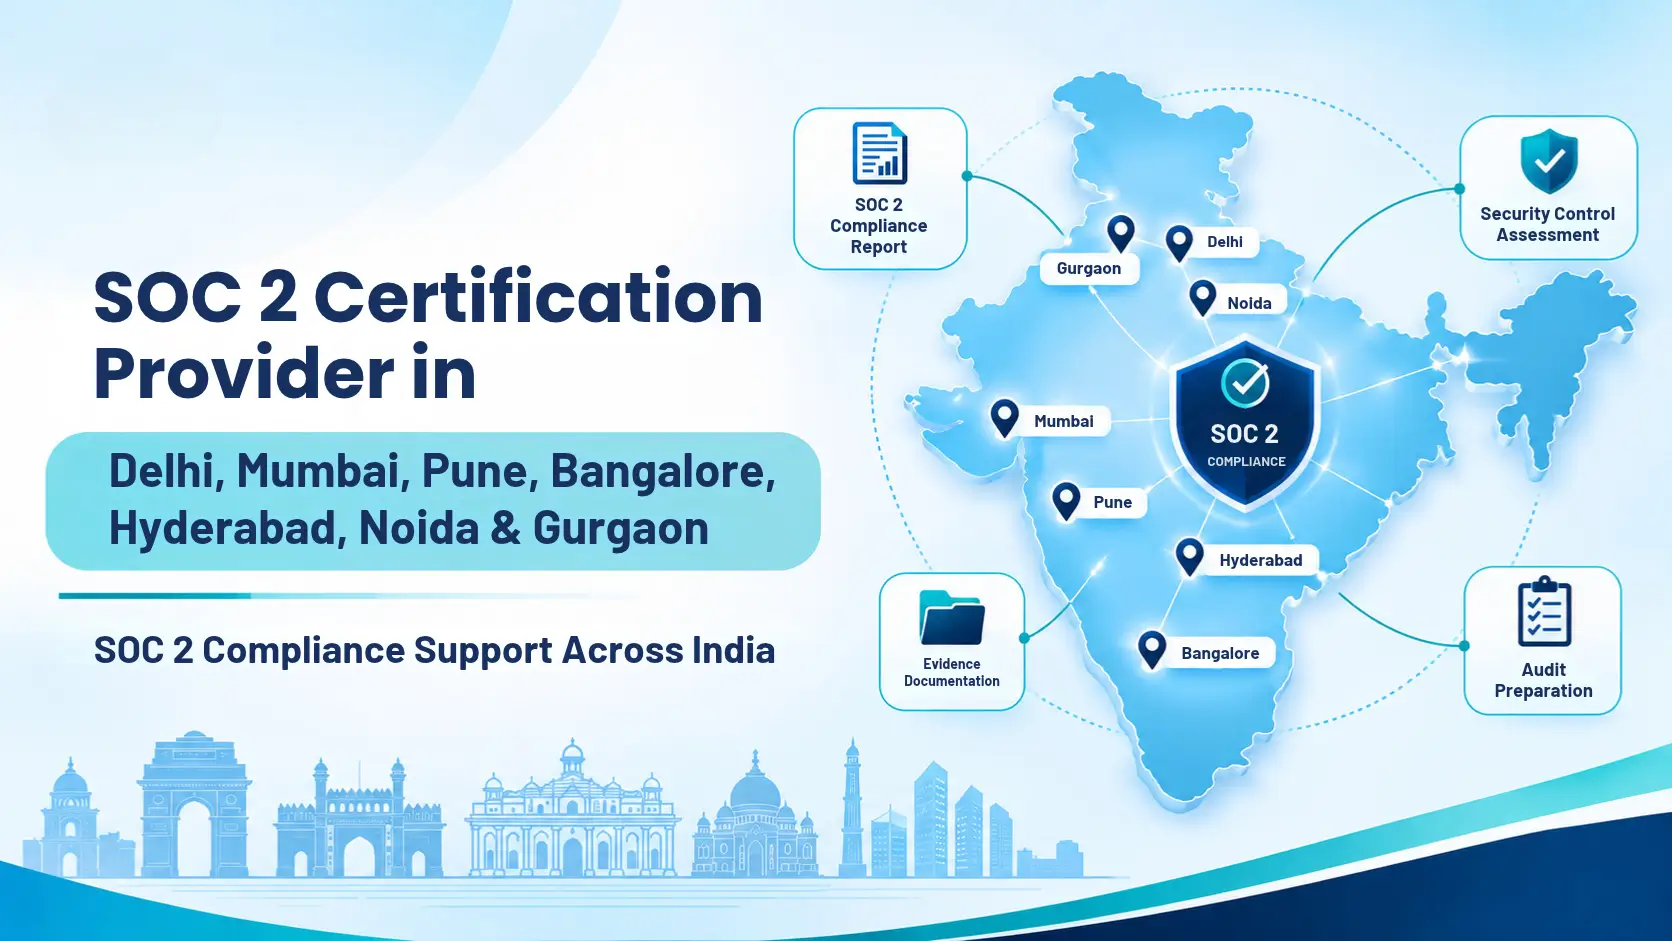
Looking for a SOC 2 provider in Delhi, Mumbai, Pune, Bangalore, Hyderabad, Noida or Gurgaon? Explore Certification support, audit requirements & SOC 2 reports.
As businesses increasingly handle sensitive customer information, maintaining strong data security practices has become essential. Customers, enterprise partners and international clients often expect service organizations to demonstrate how they protect data, manage security risks and maintain reliable systems.
This is where SOC 2 becomes important. SaaS companies, IT service providers, cloud businesses, fintech organizations and technology startups are increasingly exploring SOC 2 to meet customer security expectations and strengthen their internal controls.
Businesses searching for a SOC 2 certification provider in Delhi, Mumbai, Pune, Bangalore, Hyderabad, Noida or Gurgaon need to understand the requirements, select the appropriate report type and prepare their organization for an independent examination.
Aanetic supports businesses with SOC 2 Certification, gap assessments, control implementation guidance and evidence preparation to help them move towards SOC 2 compliance.
India has a growing technology ecosystem, with businesses serving customers across domestic and international markets. Organizations operating from major business locations are increasingly expected to demonstrate structured information security practices.
Some common reasons businesses pursue SOC 2 include:
Enterprise customer requirements: Large organizations may request SOC 2 reports before approving technology vendors.
International business opportunities: Overseas customers often evaluate security practices before entering into partnerships.
Data protection: SOC 2 encourages organizations to establish controls for protecting sensitive information.
Vendor risk management: Businesses can demonstrate how they manage security risks associated with their services.
Competitive positioning: A SOC 2 report can help organizations address security-related questions in sales and procurement.
For growing companies, preparing for SOC 2 can also help establish consistent security practices as their operations expand.
Organizations can work with SOC 2 Certification and compliance consultants regardless of their registered office location. Many preparation activities, including gap assessments, documentation reviews, evidence coordination and meetings, can be conducted remotely.
Here are some considerations for businesses operating in different Indian cities.
Delhi-based IT companies, technology consultants and service organizations often work with government clients, enterprises and international businesses. These relationships can involve security assessments and vendor compliance requirements.
A SOC 2 Certification provider can help Delhi businesses evaluate existing security practices, identify control gaps and prepare the documentation required for an independent examination.
Mumbai has a strong presence of financial services, fintech companies, SaaS businesses and technology service providers.
Organizations handling financial or customer information may face detailed security assessments from enterprise customers. SOC 2 Certification support can help them establish access management, risk assessment, monitoring and incident response controls.
Pune is an established IT and technology services destination, with numerous software development companies, SaaS providers and outsourcing businesses.
Companies in Pune looking for SOC 2 support should focus on defining their service scope, reviewing existing controls and maintaining consistent evidence of security activities.
Bangalore has a large concentration of SaaS startups, cloud technology companies, software developers, and global technology businesses.
For companies planning international expansion, SOC 2 can become an important part of customer security evaluations. A Certification consultant can help organize security policies, evaluate technical controls, and prepare teams for the examination process.
Hyderabad's technology ecosystem includes IT service companies, healthcare technology businesses, cloud providers and enterprise software organizations.
Businesses handling sensitive information can benefit from structured SOC 2 Certification activities that cover data protection, system monitoring, access controls, and vendor management.
Noida has a growing technology and IT services industry, including software companies, BPOs and digital service providers.
Organizations in Noida can work with SOC 2 consultants to understand applicable Trust Services Criteria, assess operational risks and prepare evidence before engaging an independent auditor.
Gurgaon, also known as Gurugram, is home to fintech companies, SaaS businesses, consulting firms and enterprise technology providers.
Companies working with large enterprises may encounter SOC 2 requirements during vendor onboarding. Proper Certification planning can help them address security gaps and establish the controls that customers expect.
Choosing a SOC 2 provider involves more than comparing service prices. Businesses should understand the actual support included in the engagement.
A reliable Certification partner should provide structured assistance throughout the preparation process.
An initial assessment helps identify differences between existing security practices and applicable SOC 2 requirements. It provides visibility into areas that need improvement before the examination.
The organization must identify the systems, services, infrastructure and processes covered by its SOC 2 examination. A clearly defined scope helps avoid unnecessary complexity.
Businesses may need documented policies covering information security, access management, incident response, risk management, change management and other relevant areas.
A Certification consultant helps organizations understand and implement appropriate security controls based on their operations and selected Trust Services Criteria.
SOC 2 examinations require supporting evidence. Consultants can help teams organize access reviews, system logs, monitoring records, risk assessments and other relevant documentation.
Certification partners can help organizations prepare for auditor discussions, respond to documentation requests and coordinate evidence submission. The independent auditor performs the examination and issues the SOC 2 report.
Before selecting a SOC 2 provider, businesses should understand the difference between the two main report types.
A Type 1 examination evaluates whether the organization's relevant controls are suitably designed and implemented at a specific point in time.
It can be appropriate for organizations that want to demonstrate their control framework without undergoing an extended observation period.
A Type 2 examination evaluates both the design and operating effectiveness of relevant controls over an agreed observation period.
It requires evidence demonstrating that controls operated consistently throughout the examination period.
The appropriate report depends on customer expectations, business requirements and the organization's control maturity.
Important: SOC 2 is an independent attestation examination, not a traditional certification. An independent CPA firm or qualified service auditor conducts the examination and issues the report.
Whether your business operates in Delhi, Mumbai, Pune, Bangalore, Hyderabad, Noida or Gurgaon, selecting the right Certification partner can influence the efficiency of your preparation.
Consider these factors before making a decision:
Understanding of SOC 2 requirements: Check whether the provider understands the Trust Services Criteria and examination process.
Industry experience: Look for experience supporting businesses with similar technology environments and operational requirements.
Clear service scope: Understand what is included in the engagement, from gap assessment to evidence preparation.
Practical implementation support: Choose a partner that helps address actual control gaps rather than providing documentation alone.
Transparent pricing: Request clarity on consulting fees, technology costs and independent audit fees.
Auditor independence: Confirm that Certification consulting and independent examination responsibilities are appropriately separated.
A suitable provider should explain the preparation process clearly and help your team understand its responsibilities at each stage.
Aanetic helps organizations prepare for SOC 2 examinations through structured compliance and security Certification support.
Our approach focuses on understanding your business environment, identifying gaps and helping your team establish the required controls.
Our SOC 2 support includes:
Certification Assessment: Review existing security practices and identify areas requiring improvement.
Gap Analysis: Evaluate relevant controls against applicable SOC 2 requirements.
Policy and Documentation Support: Develop and organize security policies and supporting documentation.
Control Implementation Guidance: Assist with implementing appropriate technical and operational controls.
Evidence Preparation: Help teams organize records and supporting evidence for examination.
Audit Coordination: Support communication and preparation during the independent examination process.
Whether your organization operates from Delhi, Mumbai, Pune, Bangalore, Hyderabad, Noida or Gurgaon, Aanetic can support your SOC 2 Certification journey through a structured approach.
SOC 2 Certification is an opportunity to establish stronger security practices and address the growing expectations of enterprise customers. However, successful preparation requires more than policies and documentation. Organizations must implement relevant controls and maintain evidence that supports the independent examination.
Whether your business is based in Delhi, Mumbai, Pune, Bangalore, Hyderabad, Noida or Gurgaon, Aanetic can help you understand SOC 2 requirements and prepare through a structured Certification approach.
Connect with Aanetic to discuss your SOC 2 requirements and plan the next steps towards your SOC 2 examination.
SaaS companies, cloud service providers, IT service organizations, fintech businesses and technology companies handling customer information may need SOC 2 to address customer security requirements.
The cost of SOC 2 depends on several factors, including the organization's size, system complexity, selected report type, existing security maturity, and examination scope.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
Explore Affordable SOC 2 Certification for startups with practical planning, readiness guidance, audit, and cost-conscious compliance support from Aanetic.
eed SOC 2 Urgently? Get professional readiness support from Aanetic for gap assessment, security controls, documentation and independent audit preparation.
Explore how businesses can organize SOC 2 Type 2 audit support in weeks through better evidence management, control ownership and audit coordination.