12 November 2026
|3:39 pm
|Aanetic Advisory Editorial
Can you get SOC 2 compliance for under $2,000? Explore real audit costs, practical requirements, and how Aanetic streamlines readiness.
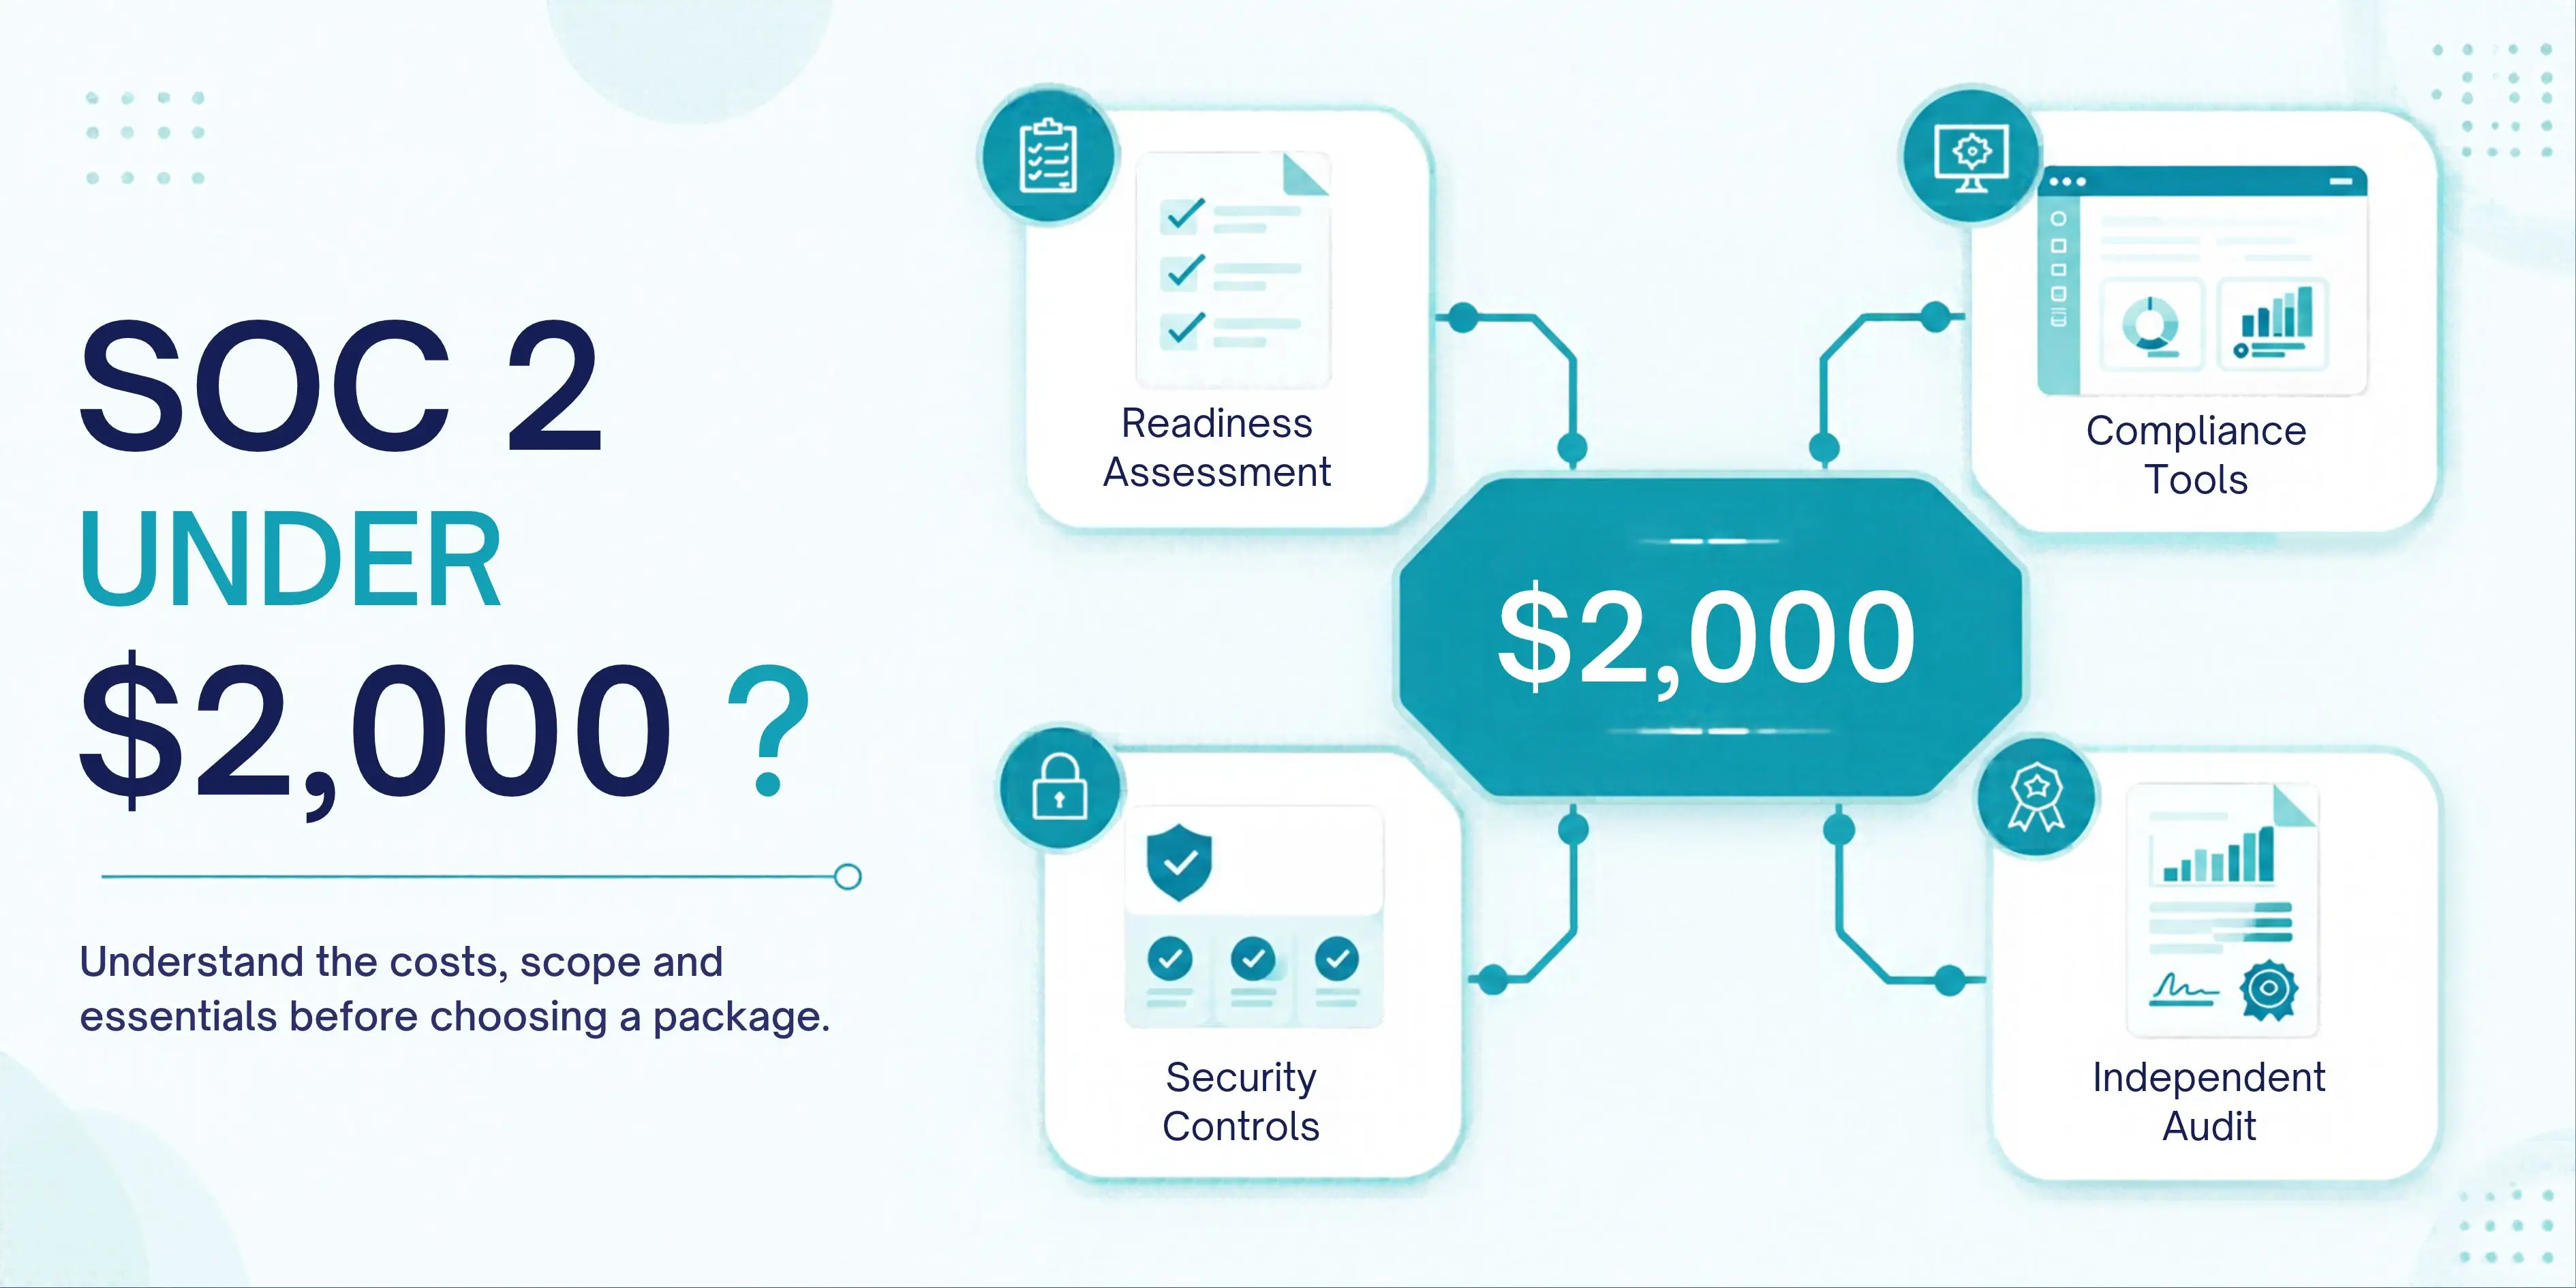
For early-stage SaaS founders and growing technology teams, winning an enterprise contract often hinges on answering a single security question: "Are you SOC 2 compliant?" When budgets are tight, the natural follow-up question is: Can you get SOC 2 compliance for under $2,000?
The honest answer is that getting a full, independent SOC 2 audit for under $2,000 is rarely possible, since you need an accredited, independent CPA firm to provide formal attestation. Still, knowing what drives SOC 2 costs for startups and how to use a readiness budget under $2,000 can help you avoid mistakes, save engineering time, and build a strong security foundation without overspending.
To evaluate whether a sub-$2,000 budget is viable, it helps to separate the two distinct phases of the journey: compliance readiness and independent CPA examination. Many organizations mistake the auditor’s fee for the entire expense, overlooking internal preparation, tooling, and remediation.
Cost Component | What It Covers | Typical Market Range (USD) |
Readiness & Gap Assessment | Evaluating existing controls against AICPA Trust Services Criteria and identifying gaps | $1,500 – $15,000 |
Policy & Documentation Setup | Drafting information security, access control, incident response, and vendor policies | Included in advisory or internal time |
Technical Remediation & Security Tools | Implementing MFA, logging, vulnerability scanning, or penetration testing | $1,000 – $25,000+ |
Independent CPA Audit Fee (Type 1) | Point-in-time evaluation of control design by a licensed CPA firm | $5,000 – $20,000 |
Independent CPA Audit Fee (Type 2) | Period-in-time evaluation (3 to 12 months) of operating effectiveness | $7,000 – $60,000+ |
Under AICPA standards, a SOC 2 report is not a self-issued badge or a basic automated checklist. It is a formal attestation report signed by an independent Certified Public Accountant (CPA) firm. Because CPA firms face strict professional liability, peer-review mandates, and manual sampling requirements, even a tightly scoped, affordable SOC 2 Type 1 audit typically starts at $5,000 to $7,500. Any offer promising a full, accredited SOC 2 report for under $2,000 should be examined carefully to confirm whether it includes an actual independent CPA sign-off or merely provides self-service software templates.
While a $2,000 budget will not cover the final CPA examination fee, it can cover a targeted initial SOC 2 audit-readiness assessment or a foundational gap analysis for a lean, cloud-native startup. By investing early in scoping and gap identification, startups avoid buying unnecessary enterprise security software and prevent expensive re-audits down the road.
Regardless of budget size, every organization pursuing SOC 2 must satisfy the AICPA Trust Services Criteria (TSCs). Most early-stage companies keep costs manageable by scoping their initial audit strictly around the Security criterion (the mandatory Common Criteria), adding Availability, Confidentiality, Processing Integrity, or Privacy only when customer contracts explicitly require them.
To pass an independent review, your team needs to set up and document consistent practices in a few key areas:
Identity and Access Management (IAM): Enforce Multi-Factor Authentication (MFA) across cloud infrastructure, version control, and production databases, paired with role-based access controls and documented employee onboarding/offboarding workflows.
Change Management: Maintain version-controlled code repositories (such as GitHub or GitLab) requiring peer code reviews and automated testing before production deployments.
Risk Assessment and Vulnerability Management: Conduct periodic risk assessments, track software patches, and run regular vulnerability scans to identify and remediate system weaknesses.
Incident Response and Business Continuity: Document an actionable incident response plan, maintain automated cloud backups, and periodically test recovery procedures.
Vendor Risk Management: Maintain an inventory of critical third-party subprocessors (e.g., AWS, Stripe, Google Workspace) and review their compliance reports annually.
Consider a 12-person B2B SaaS startup hosted entirely on AWS.
The Over-Scoped Path: The team has attempted to audit all five Trust Services Criteria simultaneously across their internal marketing tools, staging environments, and production servers. This has resulted in massive inflation in remediation work, engineering hours, and CPA testing fees.
The lean, practical path: They limit the audit to just the production application and the customer data pipeline under Security. They're using the built-in cloud security tools (AWS IAM and CloudTrail) rather than buying a whole host of third-party tools. That's a very focused approach that keeps it simple and prepares them for a Type 1 audit before a Type 2.
When working with a lean budget, the biggest hidden expense is wasted engineering time and poorly scoped audit boundaries. Aanetic helps startups and growing technology companies approach SOC 2 compliance strategically, aligning security controls with real-world operations so teams invest only where it matters.
Laser-Focused Compliance Scoping: Aanetic works closely with your leadership and technical teams to review your cloud setup, workflows, and customer needs. Setting the audit boundary early helps avoid extra controls and keeps your compliance plan practical.
Actionable Gap Assessment and Remediation Guidance: Rather than giving your developers generic warnings, Aanetic identifies specific control weaknesses and provides step-by-step technical guidance, including IAM configurations, encryption standards, logging, and vulnerability management.
Policy and Governance Documentation from scratch takes a massive amount of time. Aanetic can provide you with custom security policies (Information Security, Access Governance, Incident Response, Vendor Management), all designed specifically for fast-moving engineering teams.
Structured Evidence Organization and Auditor Coordination: Manual preparation of audit artifacts can disrupt product roadmaps. Aanetic helps organize your evidence repository and coordinates smoothly with accredited, independent CPA firms so your examination process remains clear and predictable.
Scalable Security Foundation: Beyond immediate SOC 2 readiness, Aanetic helps establish sustainable governance practices that simplify future expansion into frameworks such as ISO 27001, GDPR, or HIPAA.
So, can you get SOC 2 compliance for under $2,000? While a full, accredited CPA examination costs more, starting with a focused readiness plan ensures your money goes toward real security improvements rather than extra overhead.
If your organization is preparing to unlock enterprise deals and wants a clear, cost-conscious path to audit readiness, connect with Aanetic today. Our specialists can evaluate your current infrastructure, define an efficient audit scope, and help you build a practical SOC 2 compliance roadmap tailored to your business goals.
No, compliance automation platforms can't replace the independent CPA firm required to issue an official SOC 2 report. These tools and advisory services help organize your evidence and save time, but you'll still need to budget separately for the auditor's fee.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
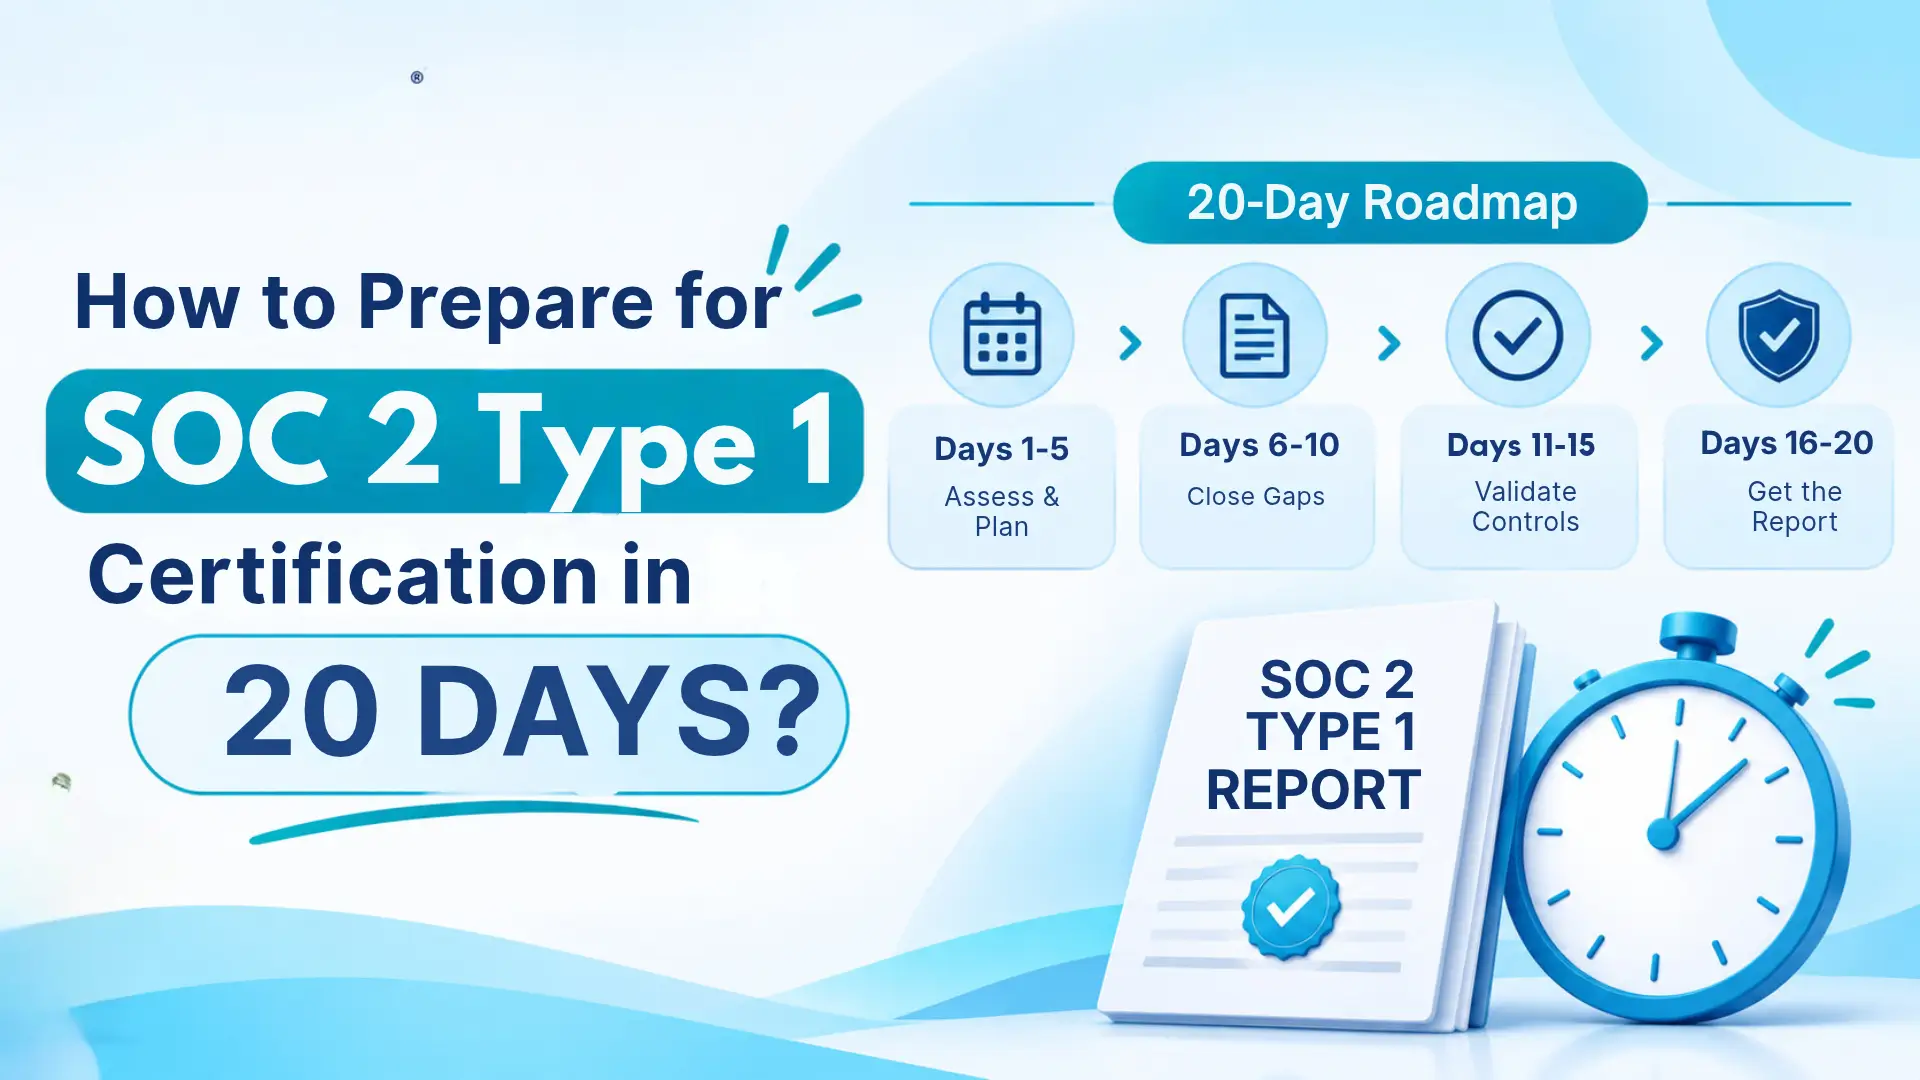
Discover how to prepare for SOC 2 Type 1 in 20 days. Follow our 20-day checklist for audit scoping, technical controls, policies, and evidence readiness.
Prepare your startup for SOC 2 without wasting time or money. Learn key scoping tips, core controls, and audit readiness steps.
Looking for the best SOC 2 provider in Noida & Delhi NCR? Explore SOC 2 readiness, gap assessment, documentation and audit preparation support with Aanetic.